weekly update at 2024-11-18
This commit is contained in:
 xx
@@ -17,36 +17,37 @@
|
||||
|
||||
| 时间 | 项目名称 | 项目动态 |
|
||||
|----|-----------|--------------------------|
|
||||
|2024-11-16|[**HaE**](detail/HaE.md)|更新 [v3.4](detail/HaE.md#最近更新) 版本|
|
||||
|2024-11-15|[**CDK**](detail/CDK.md)|更新 [v1.5.4](detail/CDK.md#最近更新) 版本|
|
||||
|2024-11-15|[**afrog**](detail/afrog.md)|更新 [v3.1.2](detail/afrog.md#最近更新) 版本|
|
||||
|2024-11-01|[**JYso**](detail/JYso.md)|更新 [v1.3.5](detail/JYso.md#最近更新) 版本|
|
||||
|2024-09-19|[**HaE**](detail/HaE.md)|更新 [v3.3.3](detail/HaE.md#最近更新) 版本|
|
||||
|2024-10-29|[**xtate**](detail/xtate.md)|xtate加入星链计划|
|
||||
|2024-09-06|[**Viper**](detail/Viper.md)|更新 [v2.3.4](detail/Viper.md#最近更新) 版本|
|
||||
|2024-08-17|[**GShark**](detail/gshark.md)|更新 [v1.5.0](detail/gshark.md#最近更新) 版本|
|
||||
|2024-08-09|[**afrog**](detail/afrog.md)|更新 [v3.1.1](detail/afrog.md#最近更新) 版本|
|
||||
|2024-08-05|[**GrabAccess**](detail/GrabAccess.md)|GrabAccess加入星链计划|
|
||||
|2024-08-03|[**ENScanGo**](detail/ENScanGo.md)|更新 [v1.0.2](detail/ENScanGo.md#最近更新) 版本|
|
||||
|2024-07-16|[**HackBrowserData**](detail/HackBrowserData.md)|更新 [v0.4.6](detail/HackBrowserData.md#最近更新) 版本|
|
||||
|2024-07-09|[**vArmor**](detail/vArmor.md)|更新 [v0.5.11](detail/vArmor.md#最近更新) 版本|
|
||||
|2024-06-06|[**dperf**](detail/dperf.md)|更新 [v1.7.0](detail/dperf.md#最近更新) 版本|
|
||||
|2024-05-26|[**AppScan**](detail/AppScan.md)|更新 [v2.1.5](detail/AppScan.md#最近更新) 版本|
|
||||
|
||||
**2.StarRank**
|
||||
|
||||
| 序号 | 项目名称 | 项目简介 | Star |
|
||||
|----|-----------|--------------------------|----|
|
||||
|1|[**HackBrowserData**](detail/HackBrowserData.md)|hack-browser-data 是一个解密浏览器数据(密码/历史记录/Cookies/书签)的导出工具,支持全平台主流浏览器的数据导出窃取。|11035|
|
||||
|2|[**fscan**](detail/fscan.md)|一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。支持主机存活探测、端口扫描、常见服务的爆破、ms17010、redis批量写公钥、计划任务反弹shell、读取win网卡信息、web指纹识别、web漏洞扫描、netbios探测、域控识别等功能。|10726|
|
||||
|1|[**HackBrowserData**](detail/HackBrowserData.md)|hack-browser-data 是一个解密浏览器数据(密码/历史记录/Cookies/书签)的导出工具,支持全平台主流浏览器的数据导出窃取。|11078|
|
||||
|2|[**fscan**](detail/fscan.md)|一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。支持主机存活探测、端口扫描、常见服务的爆破、ms17010、redis批量写公钥、计划任务反弹shell、读取win网卡信息、web指纹识别、web漏洞扫描、netbios探测、域控识别等功能。|10790|
|
||||
|3|[**dperf**](detail/dperf.md)|dperf 是一个100Gbps的网络性能与压力测试软件。国内多个知名安全厂商用dperf测试其防火墙。知名开源四层负载均衡DPVS在用dperf做性能测试,发布性能测试报告。|5040|
|
||||
|4|[**CDK**](detail/CDK.md)|CDK是一款为容器环境定制的渗透测试工具,在已攻陷的容器内部提供零依赖的常用命令及PoC/EXP。集成Docker/K8s场景特有的逃逸、横向移动、持久化利用方式,插件化管理。|3911|
|
||||
|5|[**antSword**](detail/antSword.md)|中国蚁剑是一款开源的跨平台网站管理工具。|3730|
|
||||
|6|[**Viper**](detail/Viper.md)|VIPER是一款图形化内网渗透工具,将内网渗透过程中常用的战术及技术进行模块化及武器化。|3722|
|
||||
|4|[**CDK**](detail/CDK.md)|CDK是一款为容器环境定制的渗透测试工具,在已攻陷的容器内部提供零依赖的常用命令及PoC/EXP。集成Docker/K8s场景特有的逃逸、横向移动、持久化利用方式,插件化管理。|3927|
|
||||
|5|[**antSword**](detail/antSword.md)|中国蚁剑是一款开源的跨平台网站管理工具。|3752|
|
||||
|6|[**Viper**](detail/Viper.md)|VIPER是一款图形化内网渗透工具,将内网渗透过程中常用的战术及技术进行模块化及武器化。|3745|
|
||||
|7|[**pocsuite3**](detail/pocsuite3.md)|pocsuite3是由Knownsec 404团队开发的开源远程漏洞测试和概念验证开发框架。它带有强大的概念验证引擎,以及针对最终渗透测试人员和安全研究人员的许多强大功能。|3649|
|
||||
|8|[**afrog**](detail/afrog.md)|afrog 是一款性能卓越、快速稳定、PoC 可定制的漏洞扫描工具,PoC 包含 CVE、CNVD、默认口令、信息泄露、指纹识别、未授权访问、任意文件读取、命令执行等多种漏洞类型,帮助网络安全从业者快速验证并及时修复漏洞。|3437|
|
||||
|9|[**AppInfoScanner**](detail/AppInfoScanner.md)|一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。|3188|
|
||||
|10|[**HaE**](detail/HaE.md)|HaE是一款可以快速挖掘目标指纹和关键信息的Burp插件。|3131|
|
||||
|8|[**afrog**](detail/afrog.md)|afrog 是一款性能卓越、快速稳定、PoC 可定制的漏洞扫描工具,PoC 包含 CVE、CNVD、默认口令、信息泄露、指纹识别、未授权访问、任意文件读取、命令执行等多种漏洞类型,帮助网络安全从业者快速验证并及时修复漏洞。|3452|
|
||||
|9|[**AppInfoScanner**](detail/AppInfoScanner.md)|一款适用于以HW行动/红队/渗透测试团队为场景的移动端(Android、iOS、WEB、H5、静态网站)信息收集扫描工具,可以帮助渗透测试工程师、攻击队成员、红队成员快速收集到移动端或者静态WEB站点中关键的资产信息并提供基本的信息输出,如:Title、Domain、CDN、指纹信息、状态信息等。|3200|
|
||||
|10|[**HaE**](detail/HaE.md)|HaE是一款可以快速挖掘目标指纹和关键信息的Burp插件。|3167|
|
||||
|
||||
**3.项目更新**
|
||||
|
||||
| 时间 | 项目迭代版本 |
|
||||
|----|-----------|
|
||||
|第46周|[**HaE**](detail/HaE.md) 更新 [v3.4](detail/HaE.md#最近更新) / [**CDK**](detail/CDK.md) 更新 [v1.5.4](detail/CDK.md#最近更新) / [**afrog**](detail/afrog.md) 更新 [v3.1.2](detail/afrog.md#最近更新)|
|
||||
|第44周|[**JYso**](detail/JYso.md) 更新 [v1.3.5](detail/JYso.md#最近更新)|
|
||||
|第38周|[**HaE**](detail/HaE.md) 更新 [v3.3.3](detail/HaE.md#最近更新) / [**JYso**](detail/JYso.md) 更新 [v1.3.4](detail/JYso.md#最近更新)|
|
||||
|第36周|[**Viper**](detail/Viper.md) 更新 [v2.3.4](detail/Viper.md#最近更新)|
|
||||
@@ -56,12 +57,14 @@
|
||||
|第32周|[**afrog**](detail/afrog.md) 更新 [v3.1.1](detail/afrog.md#最近更新) / [**afrog**](detail/afrog.md) 更新 [v3.1.0](detail/afrog.md#最近更新) / [**Viper**](detail/Viper.md) 更新 [v2.3.2](detail/Viper.md#最近更新)|
|
||||
|第31周|[**ENScanGo**](detail/ENScanGo.md) 更新 [v1.0.2](detail/ENScanGo.md#最近更新)|
|
||||
|第30周|[**JYso**](detail/JYso.md) 更新 [v1.3.2](detail/JYso.md#最近更新) / [**HaE**](detail/HaE.md) 更新 [v3.3](detail/HaE.md#最近更新)|
|
||||
|第29周|[**afrog**](detail/afrog.md) 更新 [v3.0.9](detail/afrog.md#最近更新) / [**GShark**](detail/gshark.md) 更新 [v1.4.6](detail/gshark.md#最近更新) / [**HackBrowserData**](detail/HackBrowserData.md) 更新 [v0.4.6](detail/HackBrowserData.md#最近更新)|
|
||||
|
||||
**4.新项目加入**
|
||||
|
||||
| 时间 | 项目名称 | 项目简介 |
|
||||
|----|-----------|--------------------------|
|
||||
|2024-10-29|[**xtate**](detail/xtate.md)|Xtate是面向互联网规模网络测量的模块化全栈扫描器(框架)。利用自研的应用层无状态扫描模型ZBanner和混合状态轻量级TCP协议栈HLTCP实现异步高速扫描。与已有的无状态端口扫描器只能探测端口是否开放不同,Xtate基于应用层无状态扫描模型,在千兆带宽下能够在6分钟内完成中国大陆地址集中所有80端口的开放性检测和Banner抓取。基于HLTCP用户态协议栈实现和TLS支持,Xtate也能够在有状态模式下执行多轮数据交互的高速扫描,包括TLS上层服务Banner抓取。Xtate框架提供统一接口以自定义模块实现不同的扫描任务,专注于大规模网络的协议层面测量(包括传输层、应用层和TLS上层服务),具有坚实的底层高速异步数据包收发机制,期望为学术和实践领域中大规模网络测量的各种算法和任务提供承载平台。|
|
||||
|2024-08-05|[**GrabAccess**](detail/GrabAccess.md)|GrabAccess:Bookit/Windows登陆密码和Bitlocker绕过工具,在物理接触目标计算机的情况下,GrabAccess可以:绕过Windows登陆密码执行任意操作(以System权限执行命令、重置Windows账户密码等),植入木马并添加自启动(可以绕过Bitlocker,但要求受害者登录),通过修改主板UEFI固件实现无视重装系统、更换硬盘的持久化(Bootkit)|
|
||||
|2024-05-13|[**vultrap**](detail/vultrap.md)|在开源领域,从来不缺少优秀的漏洞POC框架和POC,现今情况下,当有相关漏洞的漏洞情报出现的时候,其用于漏洞的验证的POC代码或利用请求都会很快的被公布在互联网上,比如Nuclei等漏洞检测框架也会即时得跟进新的漏洞,并以漏洞检测模板的形式进行更新,如nuclei 的nuclei-temaplte 仓库几乎每天都会出现新的漏洞需求和检测模板提交。对于漏洞检测模板而言,其主要目的用来验证目标是否存在漏洞,但仔细了解漏洞检测的机制之后,漏洞检测大多数情况下实际就是构造请求和判断响应的过程,那么基于次,是否可以反向思维,通过判断漏洞验证的请求来返回迷惑性的结果,扰乱扫描器的判断呢,其实本质还是honeypot的思路,也可以称“漏洞伪装”,也是本项目 vultrap的实现背景。|
|
||||
|2023-11-06|[**Pillager**](detail/Pillager.md)|Pillager是一个适用于后渗透期间的信息收集工具,可以收集目标机器上敏感信息,方便下一步渗透工作的进行。|
|
||||
|2023-10-25|[**AppScan**](detail/AppScan.md)|安全隐私卫士(AppScan)一款免费的企业级自动化App隐私合规检测工具|
|
||||
|2023-09-13|[**Tai-e**](detail/Tai-e.md)|Tai-e(太阿)是一个通用型Java程序分析框架,包含了开发程序分析技术所需的各类基础设施,并提供了可配置性高、功能强大的污点分析系统,用于检测各类隐私泄露、注入攻击等安全漏洞。|
|
||||
@@ -69,21 +72,18 @@
|
||||
|2023-08-30|[**js-cookie-monitor-debugger-hook**](detail/js-cookie-monitor-debugger-hook.md)|js cookie逆向利器:js cookie变动监控可视化工具 & js cookie hook打条件断点|
|
||||
|2023-06-26|[**JYso**](detail/JYso.md)|JYso是一个可以用于 jndi 注入攻击和生成反序列化数据流的工具,既可以当 JNDIExploit 用也可以当作 ysoserial 使用。|
|
||||
|2023-04-10|[**camille**](detail/camille.md)|现如今APP隐私合规十分重要,各监管部门不断开展APP专项治理工作及核查通报,不合规的APP通知整改或直接下架。camille可以hook住Android敏感接口,并识别是否为第三方SDK调用。根据隐私合规的场景,辅助检查是否符合隐私合规标准。|
|
||||
|2023-04-10|[**rakshasa**](detail/rakshasa.md)|rakshasa是一个使用Go语言编写的强大多级代理工具,专为实现多级代理,内网穿透而设计。它可以在节点群里面任意两个节点之间转发TCP请求和响应,同时支持socks5代理,http代理,并且可以引入外部http、socks5代理池,自动切换请求IP。|
|
||||
|2023-04-10|[**dperf**](detail/dperf.md)|dperf 是一个100Gbps的网络性能与压力测试软件。国内多个知名安全厂商用dperf测试其防火墙。知名开源四层负载均衡DPVS在用dperf做性能测试,发布性能测试报告。|
|
||||
|2022-11-17|[**WMIHACKER**](detail/WMIHACKER.md)|WMIHACKER是一款免杀横向渗透远程命令执行工具,常见的WMIEXEC、PSEXEC执行命令是创建服务或调用Win32_Process.create执行命令,这些方式都已经被杀软100%拦截,通过改造出的WMIHACKER可免杀横向移动。并且在企业网络目前阻断445端口严重的情况下可以无需445端口进行横向移动,效率高且不易被检测。|
|
||||
|
||||
**5.[分类:甲方工具](party_a.md)**
|
||||
|
||||
| 序号 | 项目名称 | 作者 | 项目简介 | Star |
|
||||
|------|----------|------|----------|------|
|
||||
|1|[**Elkeid**](detail/Elkeid.md)|bytedance|Elkeid是一个云原生的基于主机的安全(入侵检测与风险识别)解决方案。Elkeid 包含两大部分:Elkeid Agent与Elkeid Driver作为数据采集层,它在Linux系统的内核和用户空间上均可使用,从而提供了具有更好性能的且更丰富的数据。 Elkeid Server可以提供百万级Agent的接入能力,采集Agent数据,支持控制与策略下发。包含实时、离线计算模块,对采集上来的数据进行分析和检测。又有自带的服务发现和管理系统,方便对整个后台管理和操作。|2261|
|
||||
|2|[**linglong**](detail/linglong.md)|awake1t|linglong是一款甲方资产巡航扫描系统。系统定位是发现资产,进行端口爆破。帮助企业更快发现弱口令问题。主要功能包括: 资产探测、端口爆破、定时任务、管理后台识别、报表展示。|1728|
|
||||
|2|[**linglong**](detail/linglong.md)|awake1t|linglong是一款甲方资产巡航扫描系统。系统定位是发现资产,进行端口爆破。帮助企业更快发现弱口令问题。主要功能包括: 资产探测、端口爆破、定时任务、管理后台识别、报表展示。|1738|
|
||||
|3|[**murphysec**](detail/murphysec.md)|murphysecurity|墨菲安全专注于软件供应链安全,murphysec 是墨菲安全的 CLI 工具,用于在命令行检测指定目录代码的依赖安全问题,也可以基于 CLI 工具实现在 CI 流程的检测。|1672|
|
||||
|4|[**veinmind-tools**](detail/veinmind-tools.md)|长亭科技|veinmind-tools 是基于 veinmind-sdk 打造的一个容器安全工具集,目前已支持镜像 恶意文件/后门/敏感信息/弱口令 的扫描,更多功能正在逐步开发中。|1515|
|
||||
|4|[**veinmind-tools**](detail/veinmind-tools.md)|长亭科技|veinmind-tools 是基于 veinmind-sdk 打造的一个容器安全工具集,目前已支持镜像 恶意文件/后门/敏感信息/弱口令 的扫描,更多功能正在逐步开发中。|1529|
|
||||
|5|[**appshark**](detail/appshark.md)|bytedance|Appshark 是一个针对安卓的静态分析工具,它的设计目标是针对超大型App的分析,Appshark支持基于json的自定义扫描规则,发现自己关心的安全漏洞以及隐私合规问题,支持灵活配置,可以在准确率以及扫描时间空间之间寻求平衡,支持自定义扩展规则,根据自己的业务需要,进行定制分析|1515|
|
||||
|6|[**camille**](detail/camille.md)|zhengjim|现如今APP隐私合规十分重要,各监管部门不断开展APP专项治理工作及核查通报,不合规的APP通知整改或直接下架。camille可以hook住Android敏感接口,并识别是否为第三方SDK调用。根据隐私合规的场景,辅助检查是否符合隐私合规标准。|1514|
|
||||
|7|[**Tai-e**](detail/Tai-e.md)|pascal_lab|Tai-e(太阿)是一个通用型Java程序分析框架,包含了开发程序分析技术所需的各类基础设施,并提供了可配置性高、功能强大的污点分析系统,用于检测各类隐私泄露、注入攻击等安全漏洞。|1444|
|
||||
|7|[**Tai-e**](detail/Tai-e.md)|pascal_lab|Tai-e(太阿)是一个通用型Java程序分析框架,包含了开发程序分析技术所需的各类基础设施,并提供了可配置性高、功能强大的污点分析系统,用于检测各类隐私泄露、注入攻击等安全漏洞。|1457|
|
||||
|8|[**OpenStar**](detail/OpenStar.md)|starjun|OpenStar 是一个基于 OpenResty 的高性能 Web 应用防火墙,支持复杂规则编写。提供了常规的 HTTP 字段规则配置,还提供了 IP 黑白名单、访问频次等配置,对于 CC 防护更提供的特定的规则算法,并且支持搭建集群进行防护。|1260|
|
||||
|9|[**GShark**](detail/gshark.md)|madneal|一款开源敏感信息检测系统,可以监测包括 GitHub, GitLab(支持私有部署版本), Postman, searchcode 多个平台的敏感信息监测。|904|
|
||||
|10|[**AppScan**](detail/AppScan.md)|TongchengOpenSource|安全隐私卫士(AppScan)一款免费的企业级自动化App隐私合规检测工具|885|
|
||||
@@ -92,8 +92,8 @@
|
||||
|
||||
| 序号 | 项目名称 | 作者 | 项目简介 | Star |
|
||||
|------|----------|------|----------|------|
|
||||
|1|[**HaE**](detail/HaE.md)|gh0stkey|HaE是一款可以快速挖掘目标指纹和关键信息的Burp插件。|3131|
|
||||
|2|[**ENScanGo**](detail/ENScanGo.md)|wgpsec|一款基于各大企业信息API的工具,解决在遇到的各种针对国内企业信息收集难题。一键收集控股公司ICP备案、APP、小程序、微信公众号等信息聚合导出。|3091|
|
||||
|1|[**HaE**](detail/HaE.md)|gh0stkey|HaE是一款可以快速挖掘目标指纹和关键信息的Burp插件。|3167|
|
||||
|2|[**ENScanGo**](detail/ENScanGo.md)|wgpsec|一款基于各大企业信息API的工具,解决在遇到的各种针对国内企业信息收集难题。一键收集控股公司ICP备案、APP、小程序、微信公众号等信息聚合导出。|3108|
|
||||
|3|[**Kunyu**](detail/Kunyu.md)|风起|Kunyu(坤舆),是一款基于ZoomEye API开发的信息收集工具,旨在让企业资产收集更高效,使更多安全相关从业者了解、使用网络空间测绘技术。|1008|
|
||||
|4|[**Glass**](detail/Glass.md)|s7ckTeam|Glass是一款针对资产列表的快速指纹识别工具,通过调用Fofa/ZoomEye/Shodan/360等api接口快速查询资产信息并识别重点资产的指纹,也可针对IP/IP段或资产列表进行快速的指纹识别。|975|
|
||||
|5|[**ksubdomain**](detail/ksubdomain.md)|w8ay|ksubdomain是一款基于无状态子域名爆破工具,支持在Windows/Linux/Mac上使用,它会很快的进行DNS爆破,在Mac和Windows上理论最大发包速度在30w/s,linux上为160w/s的速度。|882|
|
||||
|
||||
+47
-3
@@ -28,6 +28,8 @@
|
||||
* [ct](#ct)
|
||||
* [ZoomEye-Tools](#zoomeye-tools)
|
||||
* [ZoomEye-go](#zoomeye-go)
|
||||
* [vultrap](#vultrap)
|
||||
* [xtate](#xtate)
|
||||
|
||||
* [漏洞探测/vulnerability_assessment](#漏洞探测vulnerability_assessment)
|
||||
* [afrog](#afrog)
|
||||
@@ -52,6 +54,7 @@
|
||||
* [Antenna](#antenna)
|
||||
* [Redis-Rogue-Server](#redis-rogue-server)
|
||||
* [Cola-Dnslog](#cola-dnslog)
|
||||
* [GrabAccess](#grabaccess)
|
||||
* [MysqlT](#mysqlt)
|
||||
|
||||
* [信息分析/information_analysis](#信息分析information_analysis)
|
||||
@@ -82,6 +85,7 @@
|
||||
* [BinAbsInspector](#binabsinspector)
|
||||
* [Heimdallr](#heimdallr)
|
||||
* [passive-scan-client](#passive-scan-client)
|
||||
* [GrabAccess](#grabaccess)
|
||||
* [wam](#wam)
|
||||
* [LBot](#lbot)
|
||||
|
||||
@@ -245,7 +249,7 @@ Hades 是一款支持 Windows/Linux 的内核级别数据采集主机入侵检
|
||||
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/gh0stkey/HaE>
|
||||
|
||||
@@ -341,6 +345,26 @@ ct 是一款使用 rust 语言进行开发,并且基于ZoomEye域名查询以
|
||||
|
||||
ZoomEye-go 是一款基于 ZoomEye API 开发的 Golang 库,提供了 ZoomEye 命令行模式,同时也可以作为SDK集成到其他工具中。该库可以让技术人员更便捷地搜索、筛选、导出 ZoomEye 的数据。
|
||||
|
||||
### [vultrap](detail/vultrap.md)
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/liqzz/vultrap>
|
||||
|
||||
在开源领域,从来不缺少优秀的漏洞POC框架和POC,现今情况下,当有相关漏洞的漏洞情报出现的时候,其用于漏洞的验证的POC代码或利用请求都会很快的被公布在互联网上,比如Nuclei等漏洞检测框架也会即时得跟进新的漏洞,并以漏洞检测模板的形式进行更新,如nuclei 的nuclei-temaplte 仓库几乎每天都会出现新的漏洞需求和检测模板提交。对于漏洞检测模板而言,其主要目的用来验证目标是否存在漏洞,但仔细了解漏洞检测的机制之后,漏洞检测大多数情况下实际就是构造请求和判断响应的过程,那么基于次,是否可以反向思维,通过判断漏洞验证的请求来返回迷惑性的结果,扰乱扫描器的判断呢,其实本质还是honeypot的思路,也可以称“漏洞伪装”,也是本项目 vultrap的实现背景。
|
||||
|
||||
### [xtate](detail/xtate.md)
|
||||
|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/sharkocha/xtate>
|
||||
|
||||
Xtate是面向互联网规模网络测量的模块化全栈扫描器(框架)。利用自研的应用层无状态扫描模型ZBanner和混合状态轻量级TCP协议栈HLTCP实现异步高速扫描。与已有的无状态端口扫描器只能探测端口是否开放不同,Xtate基于应用层无状态扫描模型,在千兆带宽下能够在6分钟内完成中国大陆地址集中所有80端口的开放性检测和Banner抓取。基于HLTCP用户态协议栈实现和TLS支持,Xtate也能够在有状态模式下执行多轮数据交互的高速扫描,包括TLS上层服务Banner抓取。Xtate框架提供统一接口以自定义模块实现不同的扫描任务,专注于大规模网络的协议层面测量(包括传输层、应用层和TLS上层服务),具有坚实的底层高速异步数据包收发机制,期望为学术和实践领域中大规模网络测量的各种算法和任务提供承载平台。
|
||||
|
||||
|
||||
|
||||
## 漏洞探测/vulnerability_assessment
|
||||
@@ -348,7 +372,7 @@ ZoomEye-go 是一款基于 ZoomEye API 开发的 Golang 库,提供了 ZoomEye
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/zan8in/afrog>
|
||||
|
||||
@@ -411,7 +435,7 @@ dperf 是一个100Gbps的网络性能与压力测试软件。国内多个知名
|
||||
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/cdk-team/CDK>
|
||||
|
||||
@@ -547,6 +571,16 @@ Redis 4.x/Redis 5.x RCE利用脚本. 项目最初来源于 <https://github.com/n
|
||||
|
||||
Cola Dnslog 是一款更加强大的dnslog平台(无回显漏洞探测辅助平台),支持dns http ldap rmi等协议,提供API调用方式便于与其他工具结合,支持钉钉机器人、Bark等提醒,并支持docker一键部署。
|
||||
|
||||
### [GrabAccess](detail/GrabAccess.md)
|
||||
|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/Push3AX/GrabAccess>
|
||||
|
||||
GrabAccess:Bookit/Windows登陆密码和Bitlocker绕过工具,在物理接触目标计算机的情况下,GrabAccess可以:绕过Windows登陆密码执行任意操作(以System权限执行命令、重置Windows账户密码等),植入木马并添加自启动(可以绕过Bitlocker,但要求受害者登录),通过修改主板UEFI固件实现无视重装系统、更换硬盘的持久化(Bootkit)
|
||||
|
||||
### [MysqlT](detail/MysqlT.md)
|
||||
|
||||

|
||||
@@ -796,6 +830,16 @@ BinAbsInspector(Binary Abstract Inspector)是一款用于自动化逆向工程
|
||||
|
||||
Passive Scan Client是一款可以将经过筛选的流量转发到指定代理的Burp被动扫描流量转发插件
|
||||
|
||||
### [GrabAccess](detail/GrabAccess.md)
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/Push3AX/GrabAccess>
|
||||
|
||||
GrabAccess:Bookit/Windows登陆密码和Bitlocker绕过工具,在物理接触目标计算机的情况下,GrabAccess可以:绕过Windows登陆密码执行任意操作(以System权限执行命令、重置Windows账户密码等),植入木马并添加自启动(可以绕过Bitlocker,但要求受害者登录),通过修改主板UEFI固件实现无视重装系统、更换硬盘的持久化(Bootkit)
|
||||
|
||||
### [wam](detail/wam.md)
|
||||
|
||||

|
||||
|
||||
+15
-14
@@ -3,7 +3,7 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
@@ -208,6 +208,20 @@ cdk ps
|
||||
|
||||
## 最近更新
|
||||
|
||||
#### [v1.5.4] - 2024-11-15
|
||||
|
||||
**更新**
|
||||
- 修复合并目录在路径中出现两次的问题
|
||||
- 修复添加测试 poc,Github Action 中出现未知错误的问题
|
||||
- 优化漏洞列表的输出
|
||||
- 在所有漏洞中添加类型字符串
|
||||
- 修复 github action 检查因未知问题而失败的问题
|
||||
- 添加漏洞的基本结构
|
||||
- 重新组织漏洞包中的 exp 文件
|
||||
- 在 cmd 行中运行二进制本机 kubectl 的保留路径
|
||||
- 修复在路径中找不到 gox 的问题
|
||||
- 修复使用了弃用版本而自动失败的问题
|
||||
|
||||
#### [v1.5.3] - 2024-05-19
|
||||
|
||||
**更新**
|
||||
@@ -240,17 +254,4 @@ cdk ps
|
||||
- 为 lxcfs-rw/lxcfs-rw-cgroup 添加推荐信息
|
||||
- 新增高亮显示所有的挂载信息
|
||||
|
||||
#### [v1.3.0] - 2022-07-10
|
||||
|
||||
**Exploits**
|
||||
- 为 ParseCDKMain 添加单元测试
|
||||
- 新增'Exploit container escape with kubelet log access & /var/log mount'
|
||||
- 新增 kubelet 默认未授权访问利用(端口10250)
|
||||
|
||||
**Others**
|
||||
- 在 github action 中新增了 go test
|
||||
- 支持 linux 容器获取网关
|
||||
- 更新文档,新增了 快速开始 章节
|
||||
- 新增在 pods 中获取网关
|
||||
|
||||
<!--auto_detail_active_end_f9cf7911015e9913b7e691a7a5878527-->
|
||||
|
||||
@@ -0,0 +1,173 @@
|
||||
## GrabAccess <https://github.com/Push3AX/GrabAccess>
|
||||
<!--auto_detail_badge_begin_0b490ffb61b26b45de3ea5d7dd8a582e-->
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
## GrabAccess
|
||||
|
||||
**Bookit / Windows登陆密码和Bitlocker绕过工具**
|
||||
|
||||
------
|
||||
|
||||
[**中文**](https://github.com/Push3AX/GrabAccess/blob/main/readme_cn.md) | [English](https://github.com/Push3AX/GrabAccess/blob/main/readme.md)
|
||||
|
||||
在物理接触的情况下,GrabAccess可以:
|
||||
|
||||
1. 绕过Windows登陆密码执行任意操作(以System权限执行命令、重置Windows账户密码等)
|
||||
2. 植入木马并添加自启动(可以绕过Bitlocker,但要求受害者登录)
|
||||
3. 通过修改主板UEFI固件实现无视重装系统、更换硬盘的持久化(Bootkit)
|
||||
|
||||
|
||||
|
||||
## 快速开始
|
||||
|
||||
GrabAccess最基础的功能是绕过Windows登录密码。
|
||||
|
||||
1. 准备一个U盘。(需为`FAT16`或`FAT32`格式)
|
||||
|
||||
2. 下载[GrabAccess_Release.zip](https://github.com/Push3AX/GrabAccess/releases/download/Version1.1/GrabAccess_Release_1.1.0.zip),解压到U盘根目录。
|
||||
|
||||
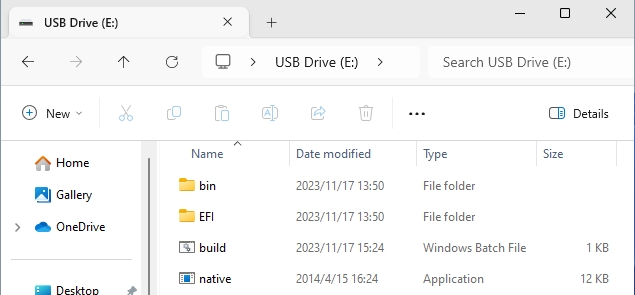
|
||||
|
||||
3. 将U盘插入目标计算机。重启,在启动时进入BIOS菜单。选择从U盘启动(如果开启了`Security Boot`,还需将其设置为`DISABLE`).
|
||||
|
||||
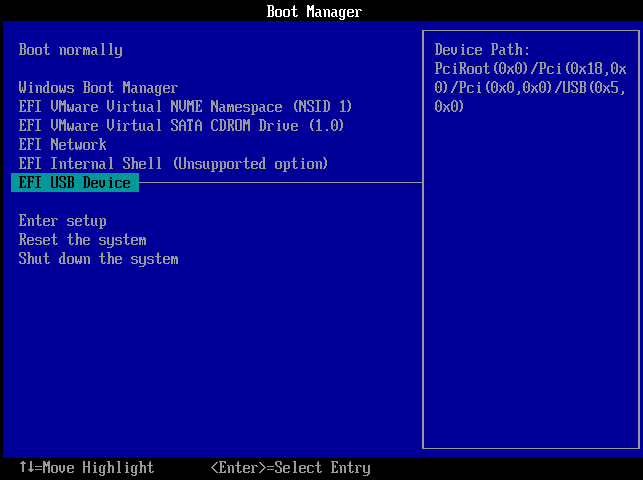
|
||||
|
||||
4. 在Windows启动时会弹出CMD窗口和账户管理窗口,可以System权限执行任意命令而无需登录。
|
||||
|
||||
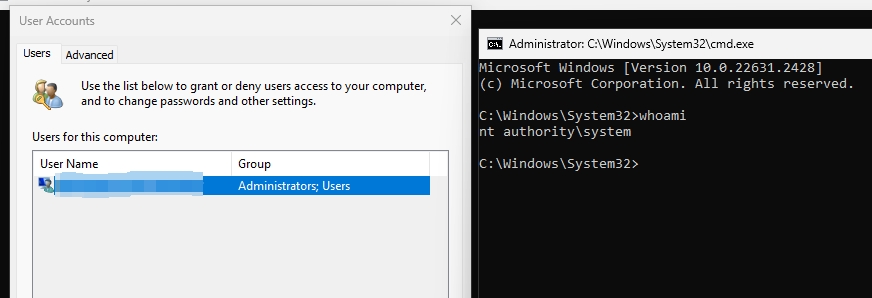
|
||||
|
||||
5. 按下`ALT+F4`关闭CMD窗口后,Windows回到登陆界面。
|
||||
|
||||
|
||||
|
||||
## 自动化植入(支持绕过 Bitlocker)
|
||||
|
||||
GrabAccess可以自动植入指定的程序,并为其添加启动项。
|
||||
|
||||
要使用该功能,需要预先将GrabAccess与要植入的程序打包:
|
||||
|
||||
1. 下载[GrabAccess_Release.zip](https://github.com/Push3AX/GrabAccess/releases/download/Version1.1/GrabAccess_Release_1.1.0.zip),解压并放置在U盘根目录。
|
||||
|
||||
2. 将需要植入的程序命名为`payload.exe`,放置在U盘根目录。
|
||||
|
||||
3. 运行`build.bat`进行打包。
|
||||
|
||||
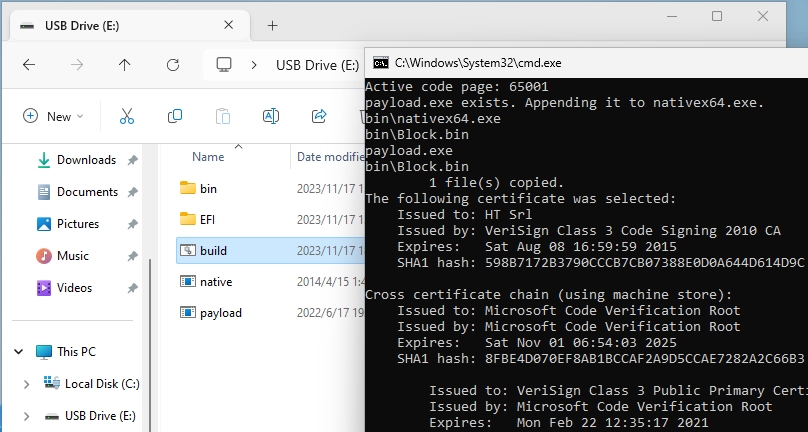
|
||||
|
||||
4. 将U盘插入目标计算机、从U盘启动(与前文相同)
|
||||
|
||||
5. Windows启动后即可看到指定的程序。
|
||||
|
||||
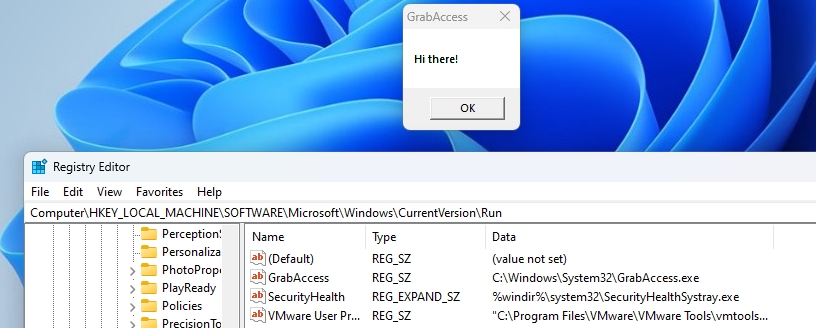
|
||||
|
||||
该植入过程可以绕过Bitlocker的系统盘加密。
|
||||
|
||||
从含有GrabAccess的U盘启动后,GrabAccess就会写入到内存中。此时可以拔出U盘,但需要停留在Bitlocker输入密码的界面,等待受害者返回输入密码。当Bitlocker解锁之后,指定的程序会被写入磁盘。但在这之前,由于GrabAccess仅停留在内存,如果重启或关机,GrabAccess将会失效。
|
||||
|
||||
|
||||
|
||||
## 修改主板UEFI固件实现Bootkit
|
||||
|
||||
GrabAccess可以被植入到计算机主板的UEFI固件。实现硬件级别的持久化(Bootkit)。
|
||||
|
||||
每次Windows系统启动时,GrabAccess会植入指定的程序,即使重装系统或更换硬盘之后也会重新植入。要移除它,只能刷写主板固件或更换主板。
|
||||
|
||||
**警告:以下操作可能损坏主板!必须对UEFI固件有一定了解才可继续。AT YOUR OWN RISK !!!!**
|
||||
|
||||
要实现这一功能,大致分为四步:
|
||||
|
||||
1. 将GrabAccess与要植入的程序打包
|
||||
2. 提取主板UEFI固件
|
||||
3. 向UEFI固件插入GrabAccessDXE
|
||||
4. 将固件刷回主板
|
||||
|
||||
不同主板的第2和第4步有较大不同。部分主板可以通过软件方式刷新固件,但也有部分主板存在校验,只能使用编程器刷新。因差异众多,在此不深入讨论,读者可以自行在网上搜索某型号主板对应的方式。
|
||||
|
||||
将GrabAccess与要植入的程序打包的方式与前文相同,即:将需要植入的程序命名为payload.exe,放置在GrabAccess的根目录,运行build.bat进行打包。结束后得到`native.exe`,稍后将会用到。
|
||||
|
||||
在提取到主板UEFI固件后,使用[UEFITool](https://github.com/LongSoft/UEFITool)打开,按下`Ctrl+F`,选择`Text`,搜索`pcibus`,在下方双击搜索到的第一项。
|
||||
|
||||
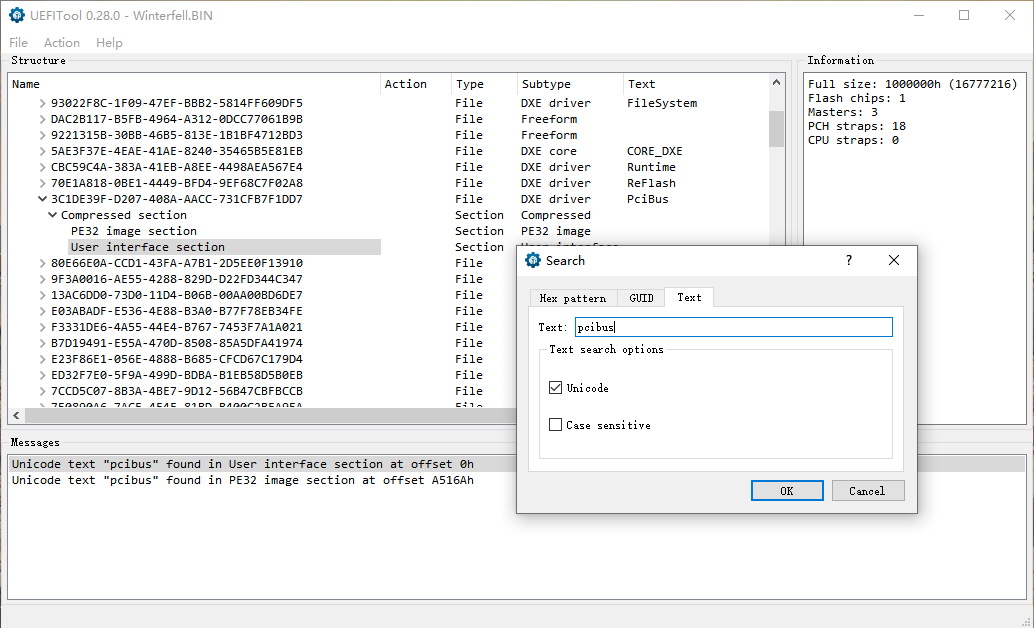
|
||||
|
||||
在`pcibus`这一项上右键,选择`Insert before`,然后选取[GrabAccess_Release.zip](https://github.com/Push3AX/GrabAccess/releases/download/Version1.1/GrabAccess_Release_1.1.0.zip)中`UEFI_FSS`文件夹的`GrabAccessDXE.ffs`。
|
||||
|
||||
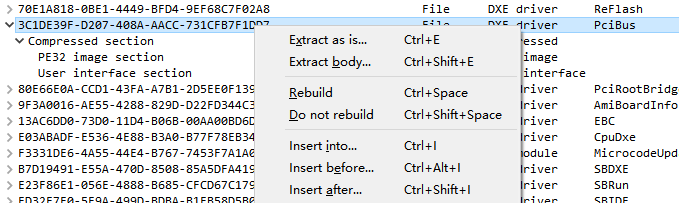
|
||||
|
||||
插入`GrabAccessDXE`后,在`GrabAccessDXE`上右键,选择`Insert before`,插入`UEFI_FSS`文件夹的`native.ffs`。此时应该如下所示:
|
||||
|
||||
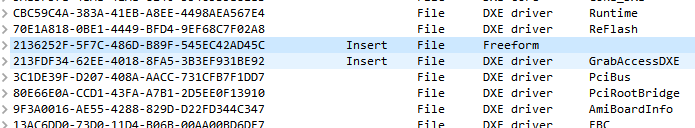
|
||||
|
||||
双击展开`native.ffs`(它没有名字,但GUID是`2136252F-5F7C-486D-B89F-545EC42AD45C`),在`Raw section`上右键,选择`Replace body`,然后选取前文中生成的`native.exe`进行替换。
|
||||
|
||||
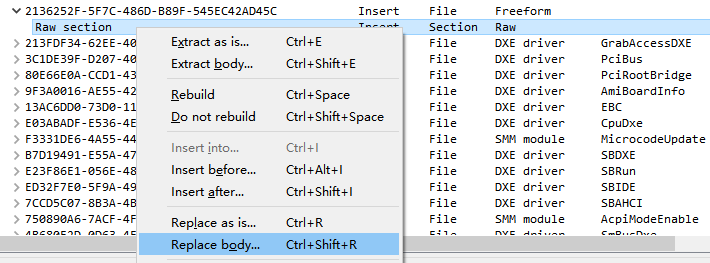
|
||||
|
||||
最后,点击File菜单的`Save image file`,保存固件到文件。
|
||||
|
||||
这份固件已经成功植入了Bootkit,将其刷回主板。如果一切顺利,在每一次Windows启动过程中,`native.exe`都会被写入并执行。
|
||||
|
||||
如果没有成功,可以尝试以下操作:
|
||||
|
||||
1. 关闭UEFI设置中的`Security Boot`和`CSM`,确定操作系统是通过UEFI模式加载的。
|
||||
2. 向固件插入`UEFI_FSS`文件夹下的`pcddxe.ffs`(方法同前文。但注意,这个模块可能会与其它模块冲突造成不能开机,仅建议在使用编程器的情况下尝试!)
|
||||
|
||||
|
||||
|
||||
## 系统支持情况
|
||||
|
||||
GrabAccess仅支持UEFI引导下的Windows系统,目前仅支持x64系统。
|
||||
|
||||
已测试Windows 10 (1803, 22H2)和Windows 11(23H2)。包括使用了TPM、联网账户、Pin码的情况。但不支持绕过Security Boot。
|
||||
|
||||
|
||||
|
||||
# 原理解析
|
||||
|
||||
## Windows Platform Binary Table
|
||||
|
||||
和Kon-boot篡改Windows内核不同,GrabAccess的工作原理,源自于Windows的一项合法后门:WPBT(Windows Platform Binary Table)。
|
||||
|
||||
WPBT常用于计算机制造商植入驱动管理软件、防丢软件。类似Bootkit病毒,一旦主板中存在WPBT条目,无论是重装系统还是更换硬盘,只要使用Windows系统,开机后都会被安装指定程序。
|
||||
|
||||
WPBT的原始设计,应当是由生产商在主板的UEFI固件中插入一个特定的模块实现。但是,通过劫持UEFI的引导过程,攻击者可以插入WPBT条目,而无需修改主板固件。
|
||||
|
||||
|
||||
|
||||
## GrabAccess做了什么
|
||||
|
||||
GrabAccess包含两个部分。
|
||||
|
||||
其一是用于写入WPBT条目的UEFI应用程序,即源码中的Stage1-UEFI。它们用于在UEFI环境下向ACPI表写入WPBT条目。
|
||||
|
||||
其二是一个Windows Native Application,即源码中的Stage2-NativeNT,用于写出最终Payload和添加启动项。
|
||||
|
||||
|
||||
|
||||
## Native Application做了什么
|
||||
|
||||
WPBT所加载的应用程序,并非常规的Win32程序。而是一个Windows Native Application。它在Windows Native NT阶段执行,早于用户登录。但是Windows提供给Native APP的API,也少于Win32程序。
|
||||
|
||||
源码中的Stage2-NativeNT负责将其末尾的最终Payload(即用户打包的指定程序)写出到`C:\\Windows\\System32\\GrabAccess.exe`,并为其添加启动项`HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run\GrabAccess`。
|
||||
|
||||
如果其末尾没有Payload,则通过IFEO劫持Logonui.exe,在Windows登录时显示cmd.exe和netplwiz.exe
|
||||
|
||||
|
||||
|
||||
## Credits
|
||||
|
||||
1. [Windows Platform Binary Table (WPBT) ](https://download.microsoft.com/download/8/a/2/8a2fb72d-9b96-4e2d-a559-4a27cf905a80/windows-platform-binary-table.docx)
|
||||
2. [WPBT-Builder ](https://github.com/tandasat/WPBT-Builder)
|
||||
3. [Windows Native App by Fox](http://fox28813018.blogspot.com/2019/05/windows-platform-binary-table-wpbt-wpbt.html)
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
## 最近更新
|
||||
|
||||
<!--auto_detail_active_end_f9cf7911015e9913b7e691a7a5878527-->
|
||||
+11
-10
@@ -3,7 +3,7 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
@@ -74,6 +74,16 @@ HaE目前的规则一共有8个字段,详细的含义如下所示:
|
||||
|
||||
## 最近更新
|
||||
|
||||
#### [v3.4] - 2024-11-16
|
||||
|
||||
**功能更新**
|
||||
- 优化HaE官方规则库规则
|
||||
- 优化UI显示界面和布局,对用户可视化操作更友好
|
||||
- 新增Mode开关,开启则支持高亮和备注,关闭则提高性能
|
||||
|
||||
**问题修复**
|
||||
- 修复汉化补丁下搜索功能失效问题
|
||||
|
||||
#### [v3.3.3] - 2024-09-19
|
||||
|
||||
**功能更新**
|
||||
@@ -116,13 +126,4 @@ HaE目前的规则一共有8个字段,详细的含义如下所示:
|
||||
- 修复HaE在暗黑主题下加载的Logo颜色问题
|
||||
- 修复项目数据导入、导出提示框过大问题
|
||||
|
||||
#### [v3.2.2] - 2024-06-19
|
||||
|
||||
**更新**
|
||||
- 修复Databoard长时间查询界面错乱问题
|
||||
- 修复Databoard在Windows下复制截断问题
|
||||
- 修复Databoard查询数据数量随机问题
|
||||
- 优化Databoard清空数据逻辑
|
||||
- 优化HTTP消息处理逻辑
|
||||
|
||||
<!--auto_detail_active_end_f9cf7911015e9913b7e691a7a5878527-->
|
||||
|
||||
+9
-7
@@ -3,7 +3,7 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
@@ -141,6 +141,14 @@ afrog -t https://example.com -ja result.json
|
||||
|
||||
## 最近更新
|
||||
|
||||
#### [v3.1.2] - 2024-11-15
|
||||
|
||||
**更新**
|
||||
- 优化PoC文件:smartbi-bypass-builtin-user-login.yaml
|
||||
- 新增资产自动去重功能
|
||||
- 优化资产存活性验证功能
|
||||
- 新增 PoC 10 个
|
||||
|
||||
#### [v3.1.1] - 2024-08-09
|
||||
|
||||
**更新**
|
||||
@@ -166,10 +174,4 @@ afrog -t https://example.com -ja result.json
|
||||
- 优化-Target命令现在能够自动从读取的文件内资产中去除左右两侧的空格
|
||||
- 修复当使用 Cookie 中包含多个冒号时无法被正确解析和应用的问题
|
||||
|
||||
#### [v3.0.7] - 2024-06-11
|
||||
|
||||
**更新**
|
||||
- 新增 OOB 平台:recvsuit,使用命令:`-oob revsuit`
|
||||
- afrog-config.yaml 新增 `revsuit` 配置
|
||||
|
||||
<!--auto_detail_active_end_f9cf7911015e9913b7e691a7a5878527-->
|
||||
|
||||
@@ -0,0 +1,28 @@
|
||||
## vultrap <https://github.com/liqzz/vultrap>
|
||||
<!--auto_detail_badge_begin_0b490ffb61b26b45de3ea5d7dd8a582e-->
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
# vultrap
|
||||
Build a vulnerability trap server
|
||||
|
||||
# Install
|
||||
```
|
||||
docker run -p 8002:8002 -it --rm qingzhaoli/vultrap:latest trapserver
|
||||
```
|
||||
|
||||
# Show
|
||||
|
||||
[](https://asciinema.org/a/yUpOFCcPOqtMJ1LJDKvG93Dtw)
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
## 最近更新
|
||||
|
||||
<!--auto_detail_active_end_f9cf7911015e9913b7e691a7a5878527-->
|
||||
+497
@@ -0,0 +1,497 @@
|
||||
## xtate <https://github.com/sharkocha/xtate>
|
||||
<!--auto_detail_badge_begin_0b490ffb61b26b45de3ea5d7dd8a582e-->
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
<h1 id="top" ></h1>
|
||||
<h1 id="whatsthis">🤔 What's this?</h1>
|
||||
|
||||
Welcome to Xtate -- A modular all-stack network scanner for next-generation internet surveys!
|
||||
|
||||
<h1 id="features">✨ Features</h1>
|
||||
|
||||
- Designed for Internet-scale scanning and surveys both in academic and practice:
|
||||
- High-speed asynchronous transmission mechanism for packets.
|
||||
- Stateless scanning model for application layer(aka. ZBanner).
|
||||
- HLTCP(Hybrid-state lightweight TCP stack) in user-space for stateful scanning.
|
||||
- etc.
|
||||
- Modularized interfaces: Custom modules in 4 types can be written to achieve your scanning task.
|
||||
- Scan Module
|
||||
- Probe Module
|
||||
- Generate Module
|
||||
- Output Module
|
||||
- Corresponding modules have been implemented for commonly used functions:
|
||||
- Port scanning and host discovery in many ways.
|
||||
- Grab service banners within one connection in a complete stateless manner.
|
||||
- Obtain TLS info and TLS-based service banner with HLTCP.
|
||||
- Service discovery and identification like LZR.
|
||||
- Probe Topology like yarrp.
|
||||
- etc.
|
||||
- Full support for IPv6 and can work in LAN.
|
||||
- ~~Written in advanced and popular C language.~~
|
||||
|
||||
|
||||
<h1 id="tableofcontent">📇 Table of Content</h1>
|
||||
|
||||
1. 🎤[Introduction](https://github.com/sharkocha/xtate/blob/xtate/README.md#introduction)
|
||||
1. 🎨[Design](https://github.com/sharkocha/xtate/blob/xtate/README.md#design)
|
||||
1. 🤺[Basic Usage](https://github.com/sharkocha/xtate/blob/xtate/README.md#basicusage)
|
||||
1. 📦[Modules](https://github.com/sharkocha/xtate/blob/xtate/README.md#modules)
|
||||
1. [Some Typical Scan Modules](https://github.com/sharkocha/xtate/blob/xtate/README.md#some-typical-scan-modules)
|
||||
1. [Some Generalizable Probe Modules](https://github.com/sharkocha/xtate/blob/xtate/README.md#some-generalizable-probe-modules)
|
||||
1. [Output Modules](https://github.com/sharkocha/xtate/blob/xtate/README.md#output-modules)
|
||||
1. [Generate Modules](https://github.com/sharkocha/xtate/blob/xtate/README.md#generate-modules)
|
||||
1. 💁[Helps in Detail](https://github.com/sharkocha/xtate/blob/xtate/README.md#-helps-in-detail)
|
||||
1. 🥽[Scan Rate](https://github.com/sharkocha/xtate/blob/xtate/README.md#scanrate)
|
||||
1. ❗[️Set Your Firewall](https://github.com/sharkocha/xtate/blob/xtate/README.md#setyourfirewall)
|
||||
1. 🔨[Build](https://github.com/sharkocha/xtate/blob/xtate/README.md#build)
|
||||
1. [Dependencies](https://github.com/sharkocha/xtate/blob/xtate/README.md#dependencies)
|
||||
1. [Compile on Linux](https://github.com/sharkocha/xtate/blob/xtate/README.md#compile-on-linux)
|
||||
1. [Compile on Windows](https://github.com/sharkocha/xtate/blob/xtate/README.md#compile-on-windows)
|
||||
1. ✍[Author](https://github.com/sharkocha/xtate/blob/xtate/README.md#author)
|
||||
1. 📄[Papers](https://github.com/sharkocha/xtate/blob/xtate/README.md#papers)
|
||||
1. 🪪[License](https://github.com/sharkocha/xtate/blob/xtate/README.md#license)
|
||||
|
||||
<h1 id="introduction">🎤 Introduction</h1>
|
||||
|
||||
Xtate provides basic ability of super fast asychronous packet sending/receiving and highly extensible architecture.
|
||||
It allows adding self-define ScanModules or ProbeModules to do different scan task with specific strategy.
|
||||
All modules could work in a packet send rate which takes up more than 90% of a gigabit of bandwidth in pcap mode and 90% of a 10 gigabit of bandwidth in PFRING mode.
|
||||
|
||||
Xtate focuses on large-scale active measurement of obtaining information about protocol themselves and corresponding underlying characteristics in real time.
|
||||
In other words, Xtate is not good at being a crawler or concentrating on content level detection like other specialized scanners.
|
||||
(Although Xtate has that abilities...)
|
||||
|
||||
Xtate was originally designed to do all scans for UDP and TCP in complete stateless manner, even obtaining responses over TCP with our **ZBanner** tech.
|
||||
But some new added features and modules make it be more than stateless.
|
||||
|
||||
For example, Xtate could do stateful TCP connection and even get HTTPS reponses after finishing TLS handshake with an improved user space stack what we called **HLTCP(hybrid-state lightweight TCP stack)** which optimized for large-scale scanning.
|
||||
However, being fast and concise is always our target.
|
||||
|
||||
In addition, Xtate supports IPv6 addresses and can be built on Windows and Linux with optional dependencies.
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="design">🎨 Design</h1>
|
||||
|
||||
Unlike existing high-speed asynchronous scanners, Xtate enables richer scanning strategies by dividing the scanning process at a fine-grained level into individual functional modules.
|
||||
This is how Xtate working internally (or you can check it by `xtate --intro`):
|
||||
|
||||
```
|
||||
+--------------------------------------------------------------------------------------------+
|
||||
| |
|
||||
| New Targets Generation Tx Threads Packet Transmit Tx Threads |
|
||||
| +----------------------+ -------------> +---------------------------+ -----------> |
|
||||
| | 1.GenerateModule | -------------> | 1.ProbeModule Hello Making| -----------> |
|
||||
| | 2.Scan Rate Control | -------------> | 2.ScanModule Transmiting | -----------> |
|
||||
| +----------------------+ +---------------------------+ |
|
||||
| |
|
||||
| ^ |
|
||||
| | |
|
||||
| Packets need to be send +-----------------------+ Send in priority | |
|
||||
| +--------------------------->| Pakcets Sending Queue +--------------------+ |
|
||||
| | +-----------------------+ |
|
||||
| | |
|
||||
| | |
|
||||
| | ScanModule Handling ScanModule Validation |
|
||||
| | +-----------------------------+ Handle Threads +-----------------------+ |
|
||||
| | | 1.ProbeModule Handling | <------------- | 1.Packet Record | Rx Thread |
|
||||
| | | 2.OutputModule save results | <------------- | 2.Deduplication | <----------- |
|
||||
| +--| 3.More packets to send | <------------- | 3.ProbeModule Validate| |
|
||||
| +-----------------------------+ +-----------------------+ |
|
||||
| |
|
||||
+--------------------------------------------------------------------------------------------+
|
||||
```
|
||||
|
||||
The most important of these are the Scan module and the Probe module.
|
||||
The Scan module is responsible for tasks in the network, transport and sometimes data-link layers during the scanning process (e.g., underlying packet construction, verification, etc.), while the Probe module is responsible for tasks above the transport layer (e.g., payload generation, content detection, etc.).
|
||||
A Scan module can be used alone (e.g. `icmp-echo` ScanModule), or paired with different Probe modules (e.g., `zbanner` ScanModulea and `http` ProbeModule). By clever design, Probe modules can even be nested with other Probe modules (e.g., `tcp-state` ScanModule, `tls-state` ProbeModule and `http` ProbeModule).
|
||||
Both Scan modules and Probe modules have own sub-parameters.
|
||||
|
||||
This is what ScanModules, ProbeModules and "all-stack" mean (or you can check it by `xtate --intro`):
|
||||
|
||||
```
|
||||
+----------------------------------------------------------------------+
|
||||
| Free supporting for new scan strategies and protocols through |
|
||||
| flexible ScanModules and ProbeModules creating and combination |
|
||||
| |
|
||||
| +--------------------+ +-------------------------+ |
|
||||
| | Application Layer +---------->| | |
|
||||
| +--------------------+ | ProbeModules | |
|
||||
| | | |
|
||||
| +--------------------+ | e.g. HTTP | |
|
||||
| | Presentation Layer +---------->| DNS | |
|
||||
| +--------------------+ | Netbios | |
|
||||
| | TLS | |
|
||||
| +--------------------+ | | |
|
||||
| | Session Layer +---------->| | |
|
||||
| +--------------------+ +-------------------------+ |
|
||||
| |
|
||||
| +--------------------+ +-------------------------+ |
|
||||
| | Transport Layer +---------->| | |
|
||||
| +--------------------+ | ScanModules | |
|
||||
| | | |
|
||||
| +--------------------+ | e.g. TCP | |
|
||||
| | Network Layer +---------->| UDP | |
|
||||
| +--------------------+ | ICMP | |
|
||||
| | NDP | |
|
||||
| +--------------------+ | ARP | |
|
||||
| | Data-link Layer +---------->| | |
|
||||
| +--------------------+ +-------------------------+ |
|
||||
| |
|
||||
| +--------------------+ |
|
||||
| | Physical Layer +----------> Stop kidding!!! |
|
||||
| +--------------------+ |
|
||||
| |
|
||||
+----------------------------------------------------------------------+
|
||||
```
|
||||
|
||||
Xtate allows and encourages users to write their own modules to accomplish specific scanning tasks.
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="basicusage">🤺 Basic Usage</h1>
|
||||
|
||||
Use `xtate --usage` to see the basic usages of xtate.
|
||||
But actually you can do much more than these if you know xtate deeply by reading helps.
|
||||
|
||||
```
|
||||
usage format:
|
||||
xtate [options] [-ip IPs -p PORTs [-scan SCANMODULE [-probe PROBEMODULE]]]
|
||||
|
||||
basic use examples of xtate:
|
||||
|
||||
xtate -p 80,8000-8100 -ip 10.0.0.0/8 --rate 10000
|
||||
use default TcpSyn ScanModule to scan web ports on 10.x.x.x at 10kpps.
|
||||
|
||||
xtate -p u:80 -ip 10.0.0.0/8 -scan udp -probe echo -show info
|
||||
use UdpProbe ScanModule to scan UDP 80 port with echo ProbeModule and also
|
||||
show info results.
|
||||
|
||||
xtate -ip 10.0.0.0/8 -scan icmp-echo -scan-arg "-ttl"
|
||||
use IcmpEcho ScanModule to do ping scan and record TTL.
|
||||
|
||||
xtate -p 80 -ip 10.0.0.0/8 -scan zbanner -probe http -scan-arg "-banner"
|
||||
use ZBanner ScanModule to grab http banners with http ProbeModule and Scan
|
||||
Module-specific param.
|
||||
|
||||
xtate -p s:38412 -ip 10.0.0.0/8 -scan sctp-init -show fail
|
||||
use SctpInit ScanModule to scan SCTP 38412(36412) port and show fail resul
|
||||
ts.
|
||||
|
||||
xtate -ip 192.168.0.1/24 -scan arp-req -lan
|
||||
do ARP scan with LAN mode in local network.
|
||||
|
||||
xtate -ip fe80::1/120 -scan ndp-ns -src-ip fe80::2 -fake-router-mac
|
||||
do NDP NS scan with a link-local source IP in local network.
|
||||
```
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="modules">📦 Modules</h1>
|
||||
|
||||
## Some Typical Scan Modules
|
||||
|
||||
Some scan modules would carry probe modules in same type for different performing.
|
||||
|
||||
I only mention some typicals of them here which do not contain much basic ones like `tcp-syn`, `icmp-echo`, etc. Details are in the help document.
|
||||
|
||||
- `zbanner`: Send probe payload after construct complete TCP connection and grab the response banner.
|
||||
All of these happen in **completely stateless manner** so that ZBanner could work in high-speed pachet send rate.
|
||||
It accept tcp type probe module.
|
||||
ZBanner tech was born from our research papar.
|
||||
|
||||
- `tcp-state`: Do scanning with an hybrid-state lightweight TCP stack what we called HLTCP.
|
||||
Actually it's stateful scan module and accept state type of probe module.
|
||||
HLTCP was born from our research paper.
|
||||
It has basic tcp funtions in large-scale scanning scenario and could touch upper layer service over TLS by pairing with `tls-state` probe module.
|
||||
|
||||
- `udp`: Send probe payload in type of udp and try to grab valid response.
|
||||
|
||||
|
||||
## Some Generalizable Probe Modules
|
||||
|
||||
However, writing modules in C is not an easy task although it helps writter understand more about principle.
|
||||
So I try to provide some highly generalizable Scan and Probe modules.
|
||||
These allows you to just use simple commands, regular expressions, or lua scripts to accomplish most of scanning tasks for POC.
|
||||
|
||||
I only present some typicals of them here.
|
||||
Details are in the help document.
|
||||
|
||||
- `hello`: Hello probe use static content set by user and reports banner. We can set a regex to match the response as successed. It is tcp type probe and we have udp and state type version, too.
|
||||
|
||||
- `recog`: Recog probe is like Hello probe but use a fingerprint file in Recog xml format to match the response by a bunch of regex. It is useful for version detection. It is tcp type probe and we have udp and state type version, too.
|
||||
|
||||
- `http`: For the most import application protocol, we provide Http probe for self-defined http header. We also can set a regex to match the response. It is tcp type probe and we have state type version, too.
|
||||
|
||||
- `lua-tcp`: Let a specified lua script with proper implementation as a tcp type probe. It will save a lot of time for use for writing simple probes.
|
||||
|
||||
- `lua-udp`: The udp type version of `lua-tcp`.
|
||||
|
||||
## Output Modules
|
||||
|
||||
I support users to write their own scan or probe modules to present unique scan strategy.
|
||||
And xtate support to result in a formatted item with standard and self-defined key-value field.
|
||||
This makes output modules to save results in various ways.
|
||||
|
||||
Xtate could save results in text, csv, ndjson, MongoDB, etc.
|
||||
You can write your own output module for better saving.
|
||||
|
||||
## Generate Modules
|
||||
|
||||
GenerateModule or Generator is an abstraction for scan targets generation. It makes target generation extensible and flexible.
|
||||
I expect that users can design their own target generation algorithms, or method like gererating from database or files, even design it with OutputModule together.
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="helpsindetail">💁 Helps in Detail</h1>
|
||||
|
||||
Xtate has many parameters for global configuration and sub-parameters for specific modules.
|
||||
All detailed help information of parameters ared embeded into the program, and I recommend using the compiled binary to view them.
|
||||
PS: Some of the help info are too long, you can use `less`(`more`) command or output it to files(or `vim`).
|
||||
|
||||
See all global parameters and help of xtate.
|
||||
|
||||
```
|
||||
xtate --help
|
||||
```
|
||||
|
||||
See all ScanModules with names and introductions.
|
||||
|
||||
```
|
||||
xtate --list-scan
|
||||
```
|
||||
|
||||
See specified ScanModules with sub-parameters and help info.
|
||||
|
||||
```
|
||||
xtate --help-scan <module-name>
|
||||
```
|
||||
|
||||
See all ProbeModules with names and introductions.
|
||||
|
||||
```
|
||||
xtate --list-probe
|
||||
```
|
||||
|
||||
See specified ProbeModules with sub-parameters and help info.
|
||||
|
||||
```
|
||||
xtate --help-probe <module-name>
|
||||
```
|
||||
|
||||
See all OutputModules with names and introductions.
|
||||
|
||||
```
|
||||
xtate --list-out
|
||||
```
|
||||
|
||||
See specified OutputModules with sub-parameters and help info.
|
||||
|
||||
```
|
||||
xtate --help-out <module-name>
|
||||
```
|
||||
|
||||
See all GenerateModules with names and introductions.
|
||||
|
||||
```
|
||||
xtate --list-gen
|
||||
```
|
||||
|
||||
See specified GenerateModules with sub-parameters and help info.
|
||||
|
||||
```
|
||||
xtate --help-gen <module-name>
|
||||
```
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="scanrate">🥽 Scan Rate</h1>
|
||||
|
||||
Xtate could do scan with a high-speed send rate like ZMap and Masscan but with more functions.
|
||||
All those tools work on similar sending way like raw socket, libpcap(winpcap) or zero-copy(PFRING/netmap).
|
||||
|
||||
Xtate inherent and improve the packet sending way of Masscan which contains multi-thread libpcap/winpcap and PFRING.
|
||||
And it randomizes the target IP addresses so that it shouldn't overwhelm any distant network.
|
||||
Xtate could event randomize the source IPv4/IPv6 addresses if needed(Yes, I fixed).
|
||||
|
||||
By default, the rate is set to 100 packets/second. To increase the rate to a million use something like --rate 1000000.
|
||||
When scanning the IPv4 Internet, you'll be scanning lots of subnets, so even though there's a high rate of packets going out, each target subnet will receive a small rate of incoming packets.
|
||||
|
||||
However, with IPv6 scanning, you'll tend to focus on a single target subnet with billions of addresses.
|
||||
Thus, your default behavior will overwhelm the target network.
|
||||
Networks often crash under the load that xtate can generate.
|
||||
|
||||
In addition, Xtate support LAN mode to do NDP or ARP scan.
|
||||
Set a proper scan rate when operate on your own network.
|
||||
|
||||
<h1 id="setyourfirewall">❗ Set Your Firewall</h1>
|
||||
|
||||
Xtate needs to avoid responds of system stack when using udp, zbanner or HLTCP scan.
|
||||
When Linux local system receives a SYN-ACK from the probed target, it responds with a RST packet that kills the connection before Xtate handle.
|
||||
Same for udp, local system may respond an icmp(port unreachable) while we receive our packets.
|
||||
|
||||
The easiest way to prevent this is to assign Xtate a separate IP address.
|
||||
Or I write some shell scripts to set iptable rules in `firewall` directory both for tcp/udp in IPv4/IPv6.
|
||||
|
||||
Note, when we do tcp-syn scan, it's better to let system stack to respond RST automaticly.
|
||||
But you can also set subparameter `--send-rst` to tcp-syn scan module to let Xtate send rst by itself while we work on Windows or use seperate source IP address on Linux.
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="build">🔨 Build</h1>
|
||||
|
||||
Xtate could be built both on Linux and Windows with CMake(>=v3.20) because of cross-platform source code.
|
||||
And some dependencies are optional, we can give up some modules if the specific dependency libraries cannot be prepared.
|
||||
|
||||
## Dependencies
|
||||
|
||||
Dependent libraries for building:
|
||||
|
||||
- OpenSSL>=1.1.1 (optional or use `-DWITH_OPENSSL=<ON/OFF>` to switch explicitly)
|
||||
- PCRE2 8bits (optional or use `-DWITH_PCRE2=<ON/OFF>` to switch explicitly)
|
||||
- LibXml2 (optional or use `-DWITH_LIBXML2=<ON/OFF>` to switch explicitly)
|
||||
- libbson>=1.7 (optional or use `-DWITH_BSON=<ON/OFF>` to switch explicitly)
|
||||
- libmongoc>=1.7 (optional or use `-DWITH_MONGOC=<ON/OFF>` to switch explicitly)
|
||||
|
||||
Optional dependencies for building won't be compiled with if Cmake didn't find the packages on your system or you can switch off it by CMake parameters.
|
||||
|
||||
Dependent libraries for running:
|
||||
|
||||
- libpcap(Linux)
|
||||
- winpcap/npcap(Windows)
|
||||
- PFRING driver(optional on Linux)
|
||||
- lua5.3/5.4(optional for lua probe support)
|
||||
|
||||
All of them can be installed on Windows in some way you like but always easier on Linux like Ubuntu(e.g. 22/24):
|
||||
|
||||
```
|
||||
sudo apt install \
|
||||
libpcap-dev \
|
||||
libssl-dev \
|
||||
libpcre2-dev \
|
||||
libxml2-dev \
|
||||
liblua5.X-0 \
|
||||
libbson-dev \
|
||||
libmongoc-dev
|
||||
```
|
||||
|
||||
Use `xtate --version` to check details of version, binary info after building.
|
||||
|
||||
## Compile on Linux
|
||||
|
||||
Recommended compile suites:
|
||||
|
||||
- GCC
|
||||
- Clang
|
||||
|
||||
After dependencies installed we can build xtate by CMake with parameters or with given script quickly:
|
||||
|
||||
```
|
||||
./build.sh [debug]
|
||||
```
|
||||
|
||||
## Compile on Windows
|
||||
|
||||
Recommended compile suites:
|
||||
|
||||
- MSVC
|
||||
- MinGW-w64
|
||||
|
||||
Generate a Visual Studio solution (e.g. VS2022) and build with MSVC:
|
||||
|
||||
```
|
||||
cd build
|
||||
cmake .. \
|
||||
[-G "Visual Studio 17 2022"] \
|
||||
[-DCMAKE_TOOLCHAIN_FILE=<maybe path of your vcpkg toolchain>]
|
||||
cmake --build . \
|
||||
--config <Release/Debug/MinSizeRel/RelWithDebInfo> \
|
||||
--parallel 4
|
||||
```
|
||||
|
||||
Generate a unix-style Makefile and build with MinGW-w64 :
|
||||
|
||||
```
|
||||
cd build
|
||||
cmake .. \
|
||||
-G "Unix Makefiles" \
|
||||
-DCMAKE_BUILD_TYPE=<Release/Debug>
|
||||
make -j4
|
||||
```
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="author">✍ Author</h1>
|
||||
|
||||
Xtate was created by Sharkocha:
|
||||
|
||||
- email: chenchiyu14@nudt.edu.cn
|
||||
|
||||
Original code was written during my master's studies at:
|
||||
|
||||
- College of Electronic Engineering, [National University of Defense Technology](https://english.nudt.edu.cn/).
|
||||
- Anhui Province Key Laboratory of Cyberspace Security Situation Awareness and Evaluation.
|
||||
|
||||
The initial version of Xtate was born from [Masscan](https://github.com/robertdavidgraham/masscan/tree/master).
|
||||
Thanks to Robert Grahm for providing valued programing throughts and code infrastructures.
|
||||
Also thanks to other excellent open-source projects I refered to and noted in the code.
|
||||
I've learned more than just finishing my worthless graduate thesis.
|
||||
|
||||
<h1 id="papers">📄 Papers</h1>
|
||||
|
||||
Some of the Scan and Probe modules with original technology are derived from our papers.
|
||||
You can see some details of Xtate in theory from them.
|
||||
I hope that Xtate will be used more in academic researches.
|
||||
And It would be my honored if you cite our papers about Xtate despite my poor academic writing for a boring degree.
|
||||
|
||||
- ZBanner: Fast Stateless Scanning Capable of Obtaining Responses over TCP
|
||||
|
||||
```
|
||||
@misc{chen2024zbanner,
|
||||
title={ZBanner: Fast Stateless Scanning Capable of Obtaining Responses over TCP},
|
||||
author={Chiyu Chen and Yuliang Lu and Guozheng Yang and Yi Xie and Shasha Guo},
|
||||
year={2024},
|
||||
eprint={2405.07409},
|
||||
archivePrefix={arXiv},
|
||||
primaryClass={cs.NI}
|
||||
}
|
||||
```
|
||||
|
||||
- Efficient Application-Layer Scanning with Hybrid-State Lightweight TCP Stack for TLS-based Service Monitoring
|
||||
|
||||
```
|
||||
publishing...
|
||||
```
|
||||
|
||||
**Well...bad papers and thesis, but wonderful scanner**😜
|
||||
|
||||
<a href="#top">🔝back to top</a>
|
||||
|
||||
<h1 id="license">🪪 License</h1>
|
||||
|
||||
Copyright (c) 2024 sharkocha
|
||||
|
||||
This program is free software: you can redistribute it and/or modify
|
||||
it under the terms of the GNU Affero General Public License as published by
|
||||
the Free Software Foundation, version 3 of the License.
|
||||
|
||||
This program is distributed in the hope that it will be useful,
|
||||
but WITHOUT ANY WARRANTY; without even the implied warranty of
|
||||
MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE. See the
|
||||
GNU Affero General Public License for more details.
|
||||
|
||||
You should have received a copy of the GNU Affero General Public License
|
||||
along with this program. If not, see <https://www.gnu.org/licenses/>.
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
## 最近更新
|
||||
|
||||
<!--auto_detail_active_end_f9cf7911015e9913b7e691a7a5878527-->
|
||||
@@ -4,8 +4,9 @@
|
||||
2. [BinAbsInspector](#binabsinspector)
|
||||
3. [Heimdallr](#heimdallr)
|
||||
4. [passive-scan-client](#passive-scan-client)
|
||||
5. [wam](#wam)
|
||||
6. [LBot](#lbot)
|
||||
5. [GrabAccess](#grabaccess)
|
||||
6. [wam](#wam)
|
||||
7. [LBot](#lbot)
|
||||
|
||||
----------------------------------------
|
||||
|
||||
@@ -49,6 +50,16 @@ BinAbsInspector(Binary Abstract Inspector)是一款用于自动化逆向工程
|
||||
|
||||
Passive Scan Client是一款可以将经过筛选的流量转发到指定代理的Burp被动扫描流量转发插件
|
||||
|
||||
### [GrabAccess](detail/GrabAccess.md)
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/Push3AX/GrabAccess>
|
||||
|
||||
GrabAccess:Bookit/Windows登陆密码和Bitlocker绕过工具,在物理接触目标计算机的情况下,GrabAccess可以:绕过Windows登陆密码执行任意操作(以System权限执行命令、重置Windows账户密码等),植入木马并添加自启动(可以绕过Bitlocker,但要求受害者登录),通过修改主板UEFI固件实现无视重装系统、更换硬盘的持久化(Bootkit)
|
||||
|
||||
### [wam](detail/wam.md)
|
||||

|
||||

|
||||
|
||||
+13
-2
@@ -15,7 +15,8 @@
|
||||
13. [Antenna](#antenna)
|
||||
14. [Redis-Rogue-Server](#redis-rogue-server)
|
||||
15. [Cola-Dnslog](#cola-dnslog)
|
||||
16. [MysqlT](#mysqlt)
|
||||
16. [GrabAccess](#grabaccess)
|
||||
17. [MysqlT](#mysqlt)
|
||||
|
||||
----------------------------------------
|
||||
|
||||
@@ -33,7 +34,7 @@ dperf 是一个100Gbps的网络性能与压力测试软件。国内多个知名
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/cdk-team/CDK>
|
||||
|
||||
@@ -169,6 +170,16 @@ Redis 4.x/Redis 5.x RCE利用脚本. 项目最初来源于 <https://github.com/n
|
||||
|
||||
Cola Dnslog 是一款更加强大的dnslog平台(无回显漏洞探测辅助平台),支持dns http ldap rmi等协议,提供API调用方式便于与其他工具结合,支持钉钉机器人、Bark等提醒,并支持docker一键部署。
|
||||
|
||||
### [GrabAccess](detail/GrabAccess.md)
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/Push3AX/GrabAccess>
|
||||
|
||||
GrabAccess:Bookit/Windows登陆密码和Bitlocker绕过工具,在物理接触目标计算机的情况下,GrabAccess可以:绕过Windows登陆密码执行任意操作(以System权限执行命令、重置Windows账户密码等),植入木马并添加自启动(可以绕过Bitlocker,但要求受害者登录),通过修改主板UEFI固件实现无视重装系统、更换硬盘的持久化(Bootkit)
|
||||
|
||||
### [MysqlT](detail/MysqlT.md)
|
||||

|
||||

|
||||
|
||||
+23
-1
@@ -11,6 +11,8 @@
|
||||
9. [ct](#ct)
|
||||
10. [Zoomeye-Tools](#zoomeye-tools)
|
||||
11. [ZoomEye-go](#zoomeye-go)
|
||||
12. [vultrap](#vultrap)
|
||||
13. [xtate](#xtate)
|
||||
|
||||
----------------------------------------
|
||||
|
||||
@@ -28,7 +30,7 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/gh0stkey/HaE>
|
||||
|
||||
@@ -124,3 +126,23 @@ ct 是一款使用 rust 语言进行开发,并且基于ZoomEye域名查询以
|
||||
|
||||
ZoomEye-go 是一款基于 ZoomEye API 开发的 Golang 库,提供了 ZoomEye 命令行模式,同时也可以作为SDK集成到其他工具中。该库可以让技术人员更便捷地搜索、筛选、导出 ZoomEye 的数据。
|
||||
|
||||
### [vultrap](detail/vultrap.md)
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/liqzz/vultrap>
|
||||
|
||||
在开源领域,从来不缺少优秀的漏洞POC框架和POC,现今情况下,当有相关漏洞的漏洞情报出现的时候,其用于漏洞的验证的POC代码或利用请求都会很快的被公布在互联网上,比如Nuclei等漏洞检测框架也会即时得跟进新的漏洞,并以漏洞检测模板的形式进行更新,如nuclei 的nuclei-temaplte 仓库几乎每天都会出现新的漏洞需求和检测模板提交。对于漏洞检测模板而言,其主要目的用来验证目标是否存在漏洞,但仔细了解漏洞检测的机制之后,漏洞检测大多数情况下实际就是构造请求和判断响应的过程,那么基于次,是否可以反向思维,通过判断漏洞验证的请求来返回迷惑性的结果,扰乱扫描器的判断呢,其实本质还是honeypot的思路,也可以称“漏洞伪装”,也是本项目 vultrap的实现背景。
|
||||
|
||||
### [xtate](detail/xtate.md)
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/sharkocha/xtate>
|
||||
|
||||
Xtate是面向互联网规模网络测量的模块化全栈扫描器(框架)。利用自研的应用层无状态扫描模型ZBanner和混合状态轻量级TCP协议栈HLTCP实现异步高速扫描。与已有的无状态端口扫描器只能探测端口是否开放不同,Xtate基于应用层无状态扫描模型,在千兆带宽下能够在6分钟内完成中国大陆地址集中所有80端口的开放性检测和Banner抓取。基于HLTCP用户态协议栈实现和TLS支持,Xtate也能够在有状态模式下执行多轮数据交互的高速扫描,包括TLS上层服务Banner抓取。Xtate框架提供统一接口以自定义模块实现不同的扫描任务,专注于大规模网络的协议层面测量(包括传输层、应用层和TLS上层服务),具有坚实的底层高速异步数据包收发机制,期望为学术和实践领域中大规模网络测量的各种算法和任务提供承载平台。
|
||||
|
||||
|
||||
@@ -12,7 +12,7 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/zan8in/afrog>
|
||||
|
||||
|
||||
Reference in New Issue
Block a user